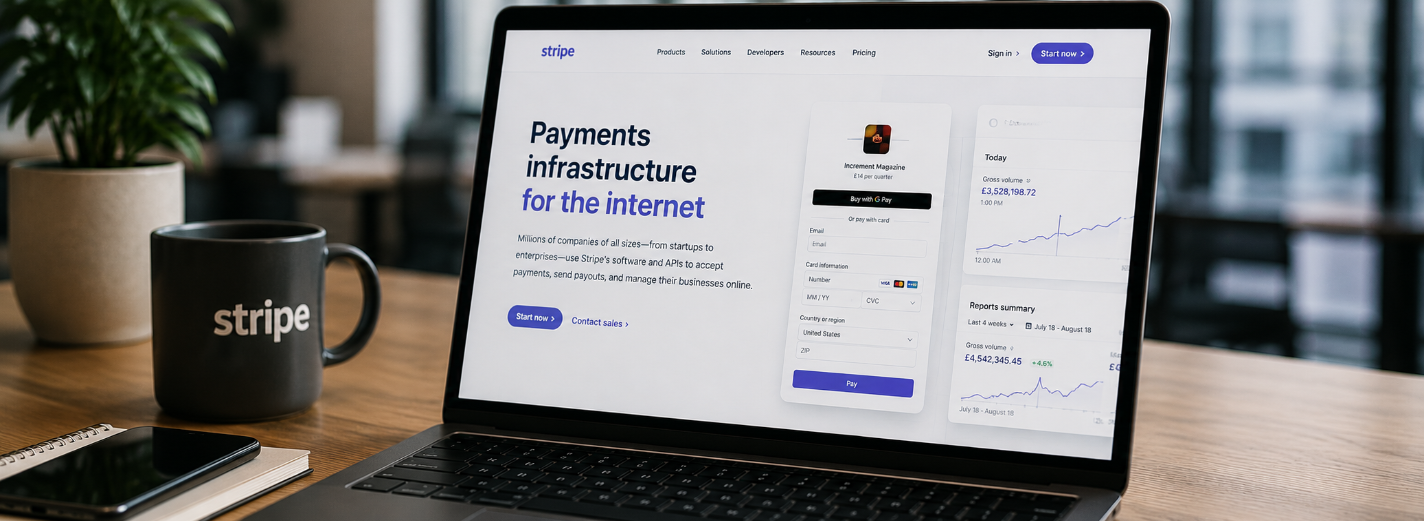
Main
Stripe Payment Integration: Architecture, Reliability, and Launch
Stripe Payment Integration: Architecture, Reliability, and Launch
- Stripe
- Payment Integration
- Fintech
- Payment Gateway
- Stripe API
- Web Development
- Subscriptions
- Stripe Connect
A payment integration looks deceptively small in a product backlog: show a form, charge a card, display success. In operation, it is a distributed financial workflow. A customer can authenticate and return later; a bank can decline or confirm asynchronously; a browser can close after the charge but before your response; the network can retry the same request; a refund can be partial; a dispute can arrive weeks after fulfilment. The difficult work is deciding which event changes the business state exactly once.
Stripe supplies payment primitives, hosted and embedded interfaces, billing, marketplace infrastructure, and operational tools. It does not decide when your order becomes payable, fulfilled, refundable, delinquent, or closed. Those are product and accounting rules. A production integration must connect Stripe objects to an internal ledger of orders, invoices, entitlements, payouts, and adjustments.
This guide treats payment development as system design. It covers the state model, trust boundaries, PaymentIntents, Checkout and Elements, webhook delivery, subscriptions, Connect, security, testing, reconciliation, and the human procedures required when automation cannot resolve a financial exception.
Begin With the Money Flow, Not the Payment Form
Start by drawing the movement of value and responsibility. Identify the buyer, merchant of record, seller or service provider, platform, payment processor, tax authority, and bank. Record who sets the price, accepts the terms, delivers the good, issues the invoice, funds a refund, carries a negative balance, answers a dispute, and owns the transaction record. The right Stripe product follows from this model; it cannot replace it.
For a simple store, the flow may be one payment followed by fulfilment. A SaaS product adds trials, proration, upgrades, failed renewals, credits, and entitlement changes. A marketplace adds connected-account onboarding, capability checks, split funds, application fees, reserves, refunds, disputes, and payouts. A mobile product also needs to respect the platform rules that apply to its goods and region.
Decide the countries, currencies, payment methods, settlement entities, tax behavior, refund policy, statement descriptors, and evidence requirements before implementation. Confirm that Stripe and the required products are available for every relevant business location. Then model the full lifecycle, including abandonment, authentication, delayed confirmation, partial fulfilment, cancellation, refund, dispute, payout failure, and account closure.
Commerce: authorize and capture orders, support wallets and local methods, preserve inventory rules, issue partial refunds, and keep fulfilment synchronized with verified payment state.
SaaS: trials, recurring invoices, plan changes, usage, proration, failed-payment recovery, credits, cancellation, and entitlement state.
Marketplaces: onboard connected accounts, allocate funds and fees, manage capabilities, refunds, disputes, transfers, reserves, and payouts.
Mobile products: server-side orchestration with native payment components, deep-link recovery, supported wallets, and applicable app-store rules.
Financial operations: invoicing, refunds, balances, reconciliation, evidence, reporting, exception queues, and controlled manual actions.
Design Stripe as Part of Your System of Record
Keep business authority on the server. The client may collect payment details through Stripe’s components and display progress, but it must not choose the payable amount, currency, product, discount, tax, recipient, or platform fee. Recalculate those values from trusted catalog and account data, bind them to an authenticated cart or invoice, and record the decision before asking Stripe to move money.
Create an internal payment record with its own stable ID and link it to the relevant Stripe Customer, Checkout Session, PaymentIntent, Invoice, Subscription, Charge, Refund, Transfer, or connected account. Store identifiers and meaningful states rather than copying sensitive payloads. Keep a journal of commands, verified events, state transitions, and accounting consequences. This gives support and finance a trace that survives browser sessions and API retries.
Separate command from observation. A synchronous API response means Stripe accepted or completed that request; it may not represent the final business outcome. Verified webhook events update the durable state, while reconciliation compares your records with Stripe’s objects, balances, payouts, and reports. Background workers handle delayed methods, retries, emails, fulfilment, and repairs without making a user wait.
Client: renders Stripe-controlled payment inputs, submits an authenticated business request, confirms when required, and displays server-derived state.
Payment API: validates identity, catalog, amount, currency, tax, recipient and permissions before issuing an idempotent Stripe command.
System of record: links internal orders, invoices and entitlements to Stripe objects and records every valid business transition.
Stripe: orchestrates payment-method rules, authentication, authorization, capture, billing objects, balances, transfers, refunds and disputes.
Webhook inbox: verifies and durably stores events, deduplicates delivery, applies valid transitions, and exposes safe replay.
Workers and operations: perform fulfilment, notifications, retries and reconciliation while monitoring owned exception queues.
Use PaymentIntents as a Payment State Machine
A PaymentIntent represents the attempt to collect a specific amount and currency for a purchase. Stripe recommends one PaymentIntent for each order or customer session, updated as the checkout evolves. Reusing it preserves the history of attempts and lets Stripe coordinate authentication and payment-method requirements while producing at most one successful charge for that intent.
Create it on the server after validating the order. Attach an internal order ID in your database and use metadata only for non-sensitive correlation. Send the client secret only to the intended customer session and never log or place it in a public URL. Treat statuses as a state machine: the payment may require a method, confirmation, customer action, capture, asynchronous processing, or a new attempt before it succeeds or is cancelled.
Use an idempotency key for every retryable create or mutation command, derived from the stable business operation rather than a random click. Idempotency protects the API command; your own handler must separately guarantee that a repeated success event does not ship twice, grant two subscriptions, or post duplicate ledger entries. For manual capture, define authorization expiry, partial capture, cancellation, inventory release, and fulfilment policy before launch.
A payment is complete when the verified financial state and your business record agree—not when a browser reaches a success page.
— GARNO.TECH Engineering
Choose Checkout or Elements by Ownership, Not Appearance
Choose the integration surface by the capability your team wants to own. Stripe-hosted Checkout is usually the strongest default when speed, payment-method coverage, localization, responsive behavior, and lower maintenance matter more than a fully bespoke flow. Embedded Checkout keeps the experience in your page while retaining a prebuilt payment journey. The Payment Element provides deeper layout control while Stripe still owns the sensitive input components and evolving payment-method presentation.
The choice is no longer a simple “redirect versus custom form.” Checkout Sessions can support hosted, embedded, and custom component approaches. Compare support for tax, discounts, shipping, subscriptions, saved methods, wallets, local methods, mobile SDKs, accessibility, analytics, and future changes. Prototype the full journey, including validation, authentication, return, retry, and cancellation, on real supported devices.
Prefer the surface that removes undifferentiated payment work. Customization creates lasting ownership: accessibility, browser changes, localization, error recovery, wallet behavior, and every new method require testing. Keep product data outside sensitive fields, disclose terms before confirmation, prevent double submission, and show a pending state when the outcome is still asynchronous. The success page should retrieve current server state; it must never manufacture success from a query parameter.
Make Webhooks Durable, Verified, and Idempotent
Webhooks are the durable bridge between Stripe’s asynchronous state and your business. Expose a dedicated HTTPS endpoint, preserve the raw request body, verify the Stripe signature with the endpoint secret, and reject stale or invalid requests. Use separate secrets for test and live endpoints. Return a successful response quickly after durable receipt, then perform fulfilment and other slow work in a queue.
Assume delivery is at least once, may be delayed, and may not match the order in which your business expects events. Store the event ID under a unique constraint, but also make the business transition idempotent: the same payment or invoice can appear through related event types. Lock or conditionally update the relevant aggregate, fetch the latest Stripe object when ordering matters, and apply a transition only if it is valid from the current state.
Keep an inbox with receipt time, processing status, attempts, correlation IDs, and a redacted error. Alert on signature failures, age of the oldest unprocessed event, repeated handler errors, and divergence between Stripe and your records. Provide replay tooling that is safe against duplicates. Periodic reconciliation remains necessary because no event pipeline should be the only evidence used to close the books.
A Security Checklist for the Whole Payment Boundary
Keep secret keys server-side in a managed secret store; scope access, rotate on exposure, and never commit credentials.
Calculate amount, currency, discounts, tax, destination and fees from trusted server data; authorize the customer for the referenced order.
Verify webhook signatures against the unmodified request body, use separate endpoint secrets, and reject invalid or stale delivery.
Apply idempotency to Stripe commands and internal state transitions; enforce uniqueness for event IDs and financial references.
Separate test and live credentials, products, prices, customers, webhooks and procedures; make the active mode unmistakable to operators.
Require MFA and least privilege for Dashboard and support tooling; review access and protect high-impact refund and payout actions.
Log internal correlation and Stripe request IDs, state transitions and actors—without card data, client secrets, personal data, or raw sensitive payloads.
Model Subscriptions and Marketplaces as Financial Operations
Recurring billing is a stateful customer relationship, not a scheduled card charge. Model the catalog, Price versions, billing interval, trial, invoice timing, taxes, coupons, credits, proration, cancellation, pause, failed-payment recovery, and the exact rule that grants or removes an entitlement. Product access should follow your verified subscription and invoice policy rather than a browser callback or one isolated event.
Keep immutable commercial history. When pricing changes, create a new Price and migrate customers through an explicit policy instead of rewriting what old invoices meant. Decide whether upgrades apply immediately, how proration is communicated, what happens at period end, how usage is measured and corrected, and how finance handles credits. Test time-dependent scenarios with Stripe test clocks where applicable, but also test your own clock, jobs, and entitlement logic.
Stripe Connect adds multiple businesses and balances to the system. Choose the charge and funds-flow model from legal and operational responsibility: who is merchant of record, who bears fees, refunds, disputes, and negative balances, and when funds become available for payout. Treat account onboarding, identity requirements, capabilities, reserves, transfers, reversals, payout failures, and offboarding as explicit workflows. Finance and support need a trace from the customer payment through platform fees and transfers to the final payout.
Six Mistakes That Turn Payments Into Incidents
Trusting the redirect: granting goods from a success URL before verified payment state reaches the server.
Creating on every click: producing multiple Intents or Sessions instead of reusing the business operation with idempotency.
Trusting client prices: accepting amount, currency, discount, tax, recipient or fee values controlled by the browser.
Non-idempotent fulfilment: shipping, granting access or posting accounting entries again when an event is retried.
Testing only success: ignoring authentication, declines, processing, timeouts, delayed methods, refunds, disputes and payouts.
Launching without operations: no reconciliation, alerts, exception ownership, support tools, rollback plan, or incident rehearsal.
Test Failure, Recovery, and Reconciliation Before Launch
A good test plan follows the state model rather than one happy card. Exercise authentication, insufficient funds, expired methods, processing states, delayed success and failure, network timeout after confirmation, duplicate commands, duplicate and out-of-order webhooks, partial capture, cancellation, partial and full refunds, disputes, subscription renewal failure, and payout failure. Verify the customer message and the accounting state, not only the HTTP response.
Use Stripe test mode, documented test payment methods, the Stripe CLI for local webhook forwarding and event triggering, and test clocks for supported billing scenarios. Contract-test your webhook parser with versioned fixtures, but keep integration tests against Stripe’s test API for assumptions a stub cannot prove. Pin and deliberately upgrade API versions and SDKs; test the account, Connect, webhook, and mobile implications before changing production.
Launch with separate live credentials and endpoint secrets, least-privilege access, dashboard MFA, registered domains, production return URLs, monitoring, and a verified support path. Start with a controlled cohort or feature flag. Observe conversion, declines, authentication, webhook lag, handler errors, fulfilment mismatches, refunds, disputes, balance movements, and payouts. Reconcile the first transactions manually from customer order to Stripe object to settlement, then automate the comparison and retain an owned exception queue.
Build a Payment Capability Your Team Can Operate
The real deliverable is not a checkout page. It is a payment capability that product, engineering, finance, risk, and support can operate together. Define ownership for catalog and price changes, credentials, API upgrades, webhook failures, reconciliation differences, refunds, disputes, negative balances, payouts, and customer communication. Give operators safe actions and an audit trail instead of asking engineers to edit rows during an incident.
Begin discovery with one representative money journey and follow it end to end: offer, tax, consent, payment initiation, authentication, confirmation, order state, fulfilment, invoice, refund, dispute, balance, payout, and ledger entry. For every transition, identify the authority, evidence, idempotency boundary, timeout, recovery path, owner, and metric. This exercise exposes missing policy before it becomes code.
GARNO.TECH can design and implement Stripe Checkout or Elements, PaymentIntents, Billing, Connect, webhook infrastructure, data migration, testing, reconciliation, observability, and operational tooling. A strong engagement leaves your team with documented states and controls, reproducible tests, monitored asynchronous flows, and a launch plan whose financial outcomes can be verified. That is the standard for a payment integration worthy of customer trust.
Publications
Our research
Research and development of AI-powered solutions to optimize business workflows and enhance decision-making processes.
Analysis of machine learning models for predictive analytics in finance, e-commerce, and SaaS platforms.
Exploration of natural language processing and computer vision technologies to strengthen automation, personalization, and customer support.
Stripe Payment Integration: Architecture, Reliability, and Launch
A practical engineering guide to Stripe Checkout, Elements, PaymentIntents, webhooks, subscriptions, Connect, security, testing, reconciliation, and payment operations.
9 min read
05 Aug 2026
React Native Development Services for Production Mobile Products
Design, build, modernize, and operate React Native products with shared domain code, deliberate platform behavior, native integrations, performance evidence, secure delivery, and sustainable ownership.
8 min read
25 Jul 2026
AWS Cloud Development: Choose Services by Workload Evidence
A production guide to AWS cloud development: workload requirements, accounts, identity, compute, data, integration, reliability, security, delivery, migration, cost and operations.
8 min read
25 Jul 2026