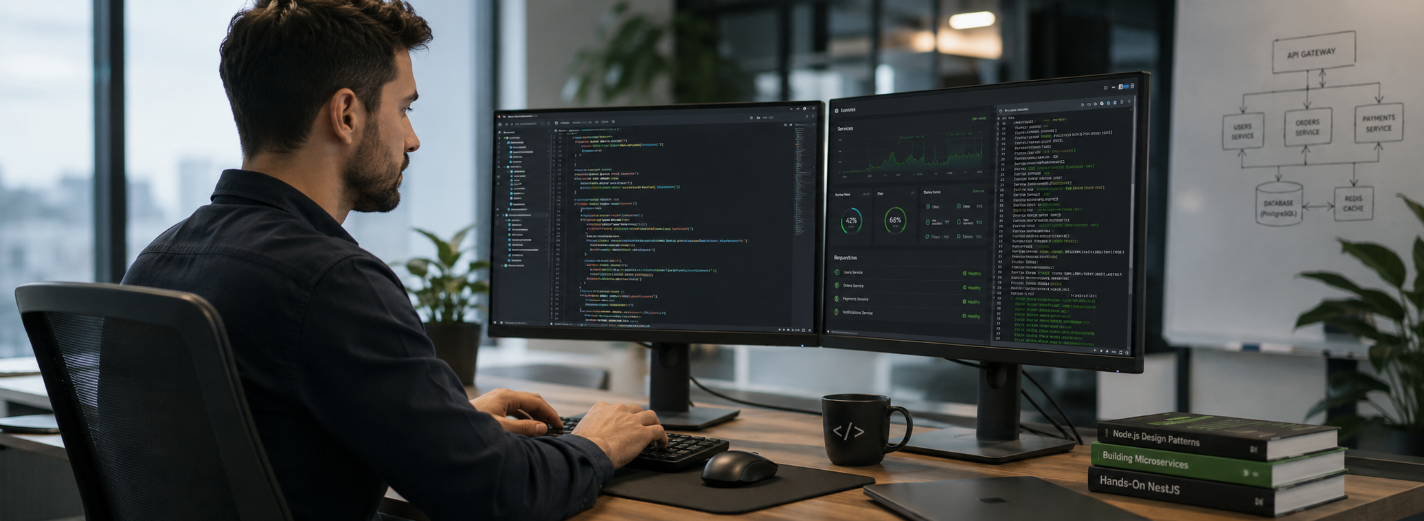
/ 01
Enforceable module APIs
Providers are private unless exported. Use this to expose application capabilities while keeping persistence and implementation details inside their domain.
NestJS is often introduced as an “enterprise Node.js framework,” but the label explains little. Its practical value is a shared grammar for backend code: modules define visibility, controllers adapt incoming requests, providers hold application capabilities, guards and pipes enforce cross-cutting policy, and dependency injection makes composition explicit. This can help a growing team locate responsibility and change behavior without rediscovering the structure on every feature.
The framework does not supply the business architecture. A large NestJS application can still become a tightly coupled collection of global modules, generic services, leaking repositories, and decorators that hide control flow. The decision therefore depends less on a feature checklist than on the system’s expected lifetime, domain complexity, team size, integration surface, operational obligations, and willingness to enforce boundaries.
Predictability reduces coordination cost. A developer joining an established NestJS codebase can expect modules, injectable providers, decorators, lifecycle hooks, and conventional testing utilities. Consistency makes reviews and ownership easier when it reflects stable rules. It becomes harmful when teams mistake folders and decorators for architecture.
Organize feature modules around business capabilities—orders, billing, identity, inventory—not technical layers shared across the entire system. Nest modules encapsulate providers by default; their exports form a public API. Use that property deliberately. Export application commands or domain-facing ports, keep persistence adapters private, and reject imports that reach through another module to its tables or internal services.
Controllers should translate transport input into application requests and map results back to the protocol. They should not contain transactions, pricing logic, or orchestration across half the system. Application services coordinate use cases; domain objects protect invariants; adapters talk to databases and external systems. Dependency injection connects these pieces through explicit tokens. Document dependency direction and test it with architecture rules, because Nest can resolve a dependency even when the design should forbid it.
A modular monolith is often the most responsible starting architecture: one deployment, one observable runtime, simple local calls, and a database transaction where consistency requires it. The modules still establish ownership and public contracts. This gives the team architectural discipline without paying immediately for distributed tracing, message compatibility, network failure, eventual consistency, fleet deployment, and cross-service incident response.
Distribution should answer measured needs. Extract a service when a capability needs independent release cadence or scaling, a distinct security boundary, separate availability, specialized technology, or genuinely autonomous ownership. High traffic alone does not require microservices; a well-designed monolith can scale horizontally. A team chart alone does not require them either; ownership can begin with modules.
Design an extraction seam before an extraction project. Remove cross-module table access, make the contract explicit, publish events through an outbox, define idempotency, and measure the call pattern. Then compare the future operational cost with the actual constraint. If a module cannot be separated inside one process, moving it across a network usually turns hidden coupling into slower and less reliable coupling.
TypeScript makes relationships visible to tools and reviewers. Typed commands, results, ports, configuration, and generated API clients reduce ambiguity and make large refactoring safer. Strict compiler settings, exhaustive unions, branded identifiers, and deliberate null handling catch many integration mistakes before runtime. They also turn the editor into a guide through a change.
Types disappear at the network and persistence boundary. A DTO annotation does not validate JSON by itself, and a database row, environment variable, message, token claim, or third-party response remains untrusted. Apply runtime validation at every external boundary, reject unknown or malformed input, normalize once, and pass trusted domain values inward. Keep transport DTOs distinct from persistence entities and domain models so one contract cannot silently rewrite the others.
Dependency injection has a similar boundary: TypeScript interfaces are erased at runtime. Use explicit tokens for ports and keep provider registration near the composition root. Avoid type assertions that merely silence uncertainty, broad any, and generated types treated as business truth. Type safety is strongest when runtime validation, database constraints, authorization, and tests defend the same invariant.
Nest can expose the same application capabilities through REST, GraphQL, WebSockets, queues, scheduled jobs, command-line tools, and microservice transports. This breadth is useful when adapters remain adapters. An order-placement use case should enforce the same pricing, inventory, authorization, and idempotency rules whether invoked from HTTP, a message, or an administrator tool.
Choose a transport for its semantics. REST is clear for resource-oriented public APIs; GraphQL can serve client-driven graphs but needs authorization, batching, and complexity controls; WebSockets support low-latency updates but introduce connection state and backpressure; queues decouple time and absorb bursts but require durable outcomes, duplicate handling, and backlog operations. Nest’s common pipes, guards, interceptors, and exception concepts reduce learning cost, yet they do not erase these differences.
Avoid a universal abstraction that hides delivery guarantees or forces every protocol into request-response. Define contracts at the application boundary and implement transport-specific concerns outside it. Version public APIs and messages deliberately. Add correlation and causation IDs to asynchronous paths. Test the real adapter and failure behavior, not merely the provider with every dependency mocked.
Nest supplies extension points for authentication, authorization, validation, rate limiting, security headers, CORS, CSRF protection, serialization, and exception handling. A secure system still needs a threat model and consistent policy. Authenticate centrally, authorize at the business action and resource level, validate and normalize untrusted input, minimize returned data, protect secrets, and deny by default. Test that each transport applies the intended policy; an HTTP guard does not automatically secure a queue consumer.
Use the dependency graph to make testing precise. Unit-test domain rules as plain TypeScript. Instantiate focused testing modules for application services and replace ports deliberately. Run integration tests against real database constraints, transactions, message serialization, caches, and third-party adapters. Keep a small end-to-end suite for critical journeys, authentication, global pipes, filters, and production bootstrap configuration.
Do not mock away the largest risks. A repository double cannot prove a unique constraint, rollback, isolation level, or migration. A fake broker cannot prove delivery semantics. A controller test cannot prove proxy, timeout, body-size, or graceful-shutdown behavior. The test portfolio should follow consequences and boundaries, while dependency injection makes substitution controlled rather than universal.
NestJS runs wherever its Node.js runtime and dependencies run. On Azure, AWS, Google Cloud, Kubernetes, containers, or a simpler platform, design the application around portable operational contracts: validated configuration, stateless request handling where practical, external durable state, health and readiness signals, graceful shutdown, structured logs, traces, metrics, and repeatable deployment artifacts.
Cloud services are architectural choices, not annotations. For every managed database, queue, cache, identity provider, secret store, or object store, define timeouts, retries, idempotency, connection limits, data residency, recovery targets, cost boundaries, and the behavior when the service is slow or unavailable. Hide vendor SDKs behind narrow adapters where substitution or domain isolation matters, but preserve provider-specific semantics rather than pretending all services are interchangeable.
Scale from evidence. Measure event-loop delay, memory, garbage collection, request latency, throughput, connection-pool saturation, queue age, and downstream limits. Use the appropriate HTTP adapter only after profiling the representative workload. Keep build and runtime images small, run migrations as a controlled release step, deploy progressively, and prove rollback and restoration. Cloud elasticity cannot repair an unbounded query, blocking CPU work, or a dependency already at its quota.
NestJS may be too much structure for a short-lived script, a tiny proxy, a narrow serverless handler, or an experiment whose primary question is still product demand. Modules, decorators, reflection, dependency injection, and bootstrap conventions have learning and debugging cost. A smaller framework or plain library composition can be clearer when the application has few endpoints, little shared policy, and one or two maintainers.
It can also be the wrong fit for CPU-intensive computation that belongs in specialized workers, for teams committed to a different runtime ecosystem, or when cold-start and bundle constraints dominate. A framework migration rarely fixes unclear ownership, unstable requirements, poor data design, or missing operations. Measure those problems before prescribing Nest.
Run a thin technical spike around the hardest representative journey: authentication, transaction, external integration, background effect, deployment, and telemetry. Compare NestJS with at least one credible alternative using delivery time, clarity, performance, library maturity, hiring and team experience, security patching, testability, observability, and long-term change cost. Include the cost of leaving the chosen framework, not only entering it.
NestJS repays its ceremony when the team uses modules and dependency injection to make responsibility visible, contracts narrow, and change safer over years of product growth.— GARNO.TECH
The strongest reason to choose NestJS is organizational: the application will live long enough, grow complex enough, and involve enough people that consistent composition and enforceable boundaries repay their cost. The weakest reason is fashion or the assumption that decorators automatically make software enterprise-ready.
Begin with the business map. Identify capabilities, invariants, owners, transactions, integrations, security boundaries, latency and recovery targets, and expected change. Create modules around those capabilities, expose narrow contracts, keep the domain independent of delivery mechanisms, and start with the simplest deployment that meets the evidence. Add distributed components only when a measured constraint justifies their permanent operating cost.
Review the architecture by following one important request from authentication through validation, business decision, persistence, external effects, telemetry, and recovery. If each step has an owner, a testable contract, observable evidence, and a safe failure path, NestJS is supporting the system. If the journey disappears inside global providers and circular imports, more framework features will not rescue it.
GARNO.TECH can assess an existing Node.js backend or design a new NestJS system from the first domain map through production rollout. NestJS development services can cover modular architecture, API and event contracts, data access, integrations, security, testing, performance, cloud delivery, observability, migration, and team enablement. Bring one critical business journey, the systems it touches, current failure evidence, and the change you expect over the next two years; that is enough to begin an architecture grounded in reality.
export const ORDERS = Symbol('ORDERS');

@Module({
  controllers: [OrdersController],
  providers: [
    PlaceOrder,
    { provide: ORDERS, useClass: SqlOrderRepository },
  ],
  exports: [PlaceOrder],
})
export class OrdersModule {}Research and development of AI-powered solutions to optimize business workflows and enhance decision-making processes.
Analysis of machine learning models for predictive analytics in finance, e-commerce, and SaaS platforms.
Exploration of natural language processing and computer vision technologies to strengthen automation, personalization, and customer support.
Build a defensible SaaS budget from release scope, tenancy, architecture, UX, integrations, security, team capability, uncertainty and total operating cost.
8 min read
Design an Azure landing zone around workload ownership, management groups, subscriptions, identity, networking, policy, telemetry, cost and automated onboarding.
9 min read
Design reproducible load tests around user outcomes, realistic traffic, percentiles, full-path telemetry, autoscaling, saturation, failure, recovery, data integrity, and a safe operating envelope.
10 min read