/ 01
Enforceable Domain Boundaries
Organize modules around business capabilities with narrow public APIs, explicit data and transaction ownership, private internals, import rules, architecture tests, and code ownership.
NestJS supplies modules, providers, dependency injection, controllers, guards, pipes, interceptors, filters, and adapters. These mechanisms can support a well-structured TypeScript backend, but they do not choose domain boundaries, authorize business actions, define transaction semantics, make remote calls safe, or establish production ownership. Architecture emerges from those decisions and from the rules that keep them true as the codebase and team change.
A production backend connects business workflows, data, identities, integrations, asynchronous work, delivery, telemetry, recovery, and support. Begin with critical state transitions: who may perform them, for which tenant and resource, from what prior state, with which authoritative data, under what consistency and timing requirements, and how an incomplete or disputed outcome is explained and repaired. Framework folders become useful only after this behavior is explicit.
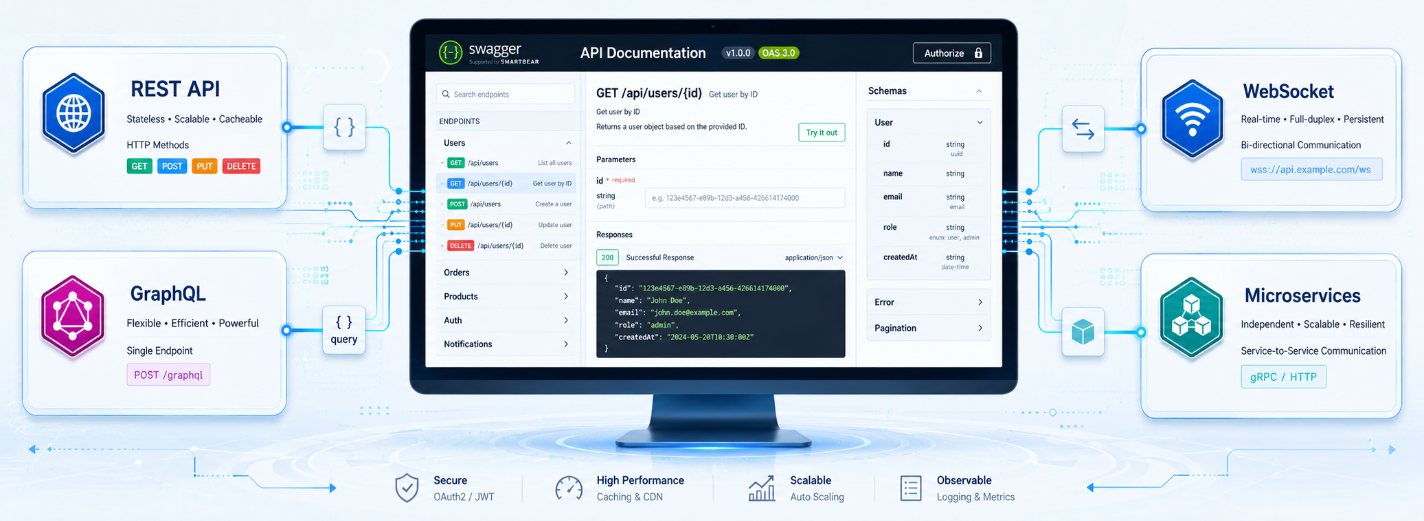
The responsible default is usually a modular monolith with narrow internal contracts and one deployment, unless independent scaling, isolation, release cadence, or ownership justifies distribution. This preserves local reasoning and transactions while leaving seams for later extraction. Microservices introduced before boundaries and operations are mature convert code uncertainty into network, data, deployment, and incident uncertainty.
Organize modules around business capabilities such as identity, tenancy, orders, billing, entitlements, fulfilment, or reporting. Export the smallest useful application interface and keep internal entities, repositories, provider SDKs, and implementation details private. Controllers translate transports; application handlers coordinate use cases; domain code holds policy and state transitions; adapters implement persistence, messaging, files, and suppliers. Dependencies should point toward stable business behavior.
Make boundaries enforceable. Use workspace or project boundaries, lint rules, import restrictions, public entry points, code ownership, architecture tests, and review. Avoid a global “shared” module that becomes an unowned path around every boundary. Share stable primitives and infrastructure contracts deliberately; keep business concepts inside the module that owns their meaning.
Define transaction ownership with the data model. One use case should identify its authoritative write, concurrency rule, invariants, and commit boundary. Cross-module work may use a local transaction when data ownership allows it, or durable events, an outbox, idempotent consumers, compensation, and reconciliation when work crosses asynchronous or service boundaries. A database transaction cannot include a remote provider merely because the call occurs inside the same method.
Treat every inbound boundary as untrusted. Parse and validate runtime input, reject unknown or oversized content where appropriate, normalize carefully, set body and file limits, protect uploads and outbound fetches, and return stable error contracts without leaking secrets or internal structure. TypeScript types disappear at runtime; DTO declarations protect nothing until validation is actually bound and tested for HTTP, GraphQL, messages, jobs, and administrative paths.
Authentication establishes an identity; authorization decides whether that identity may perform this operation on this tenant and resource in the current state. Use guards or boundary policy checks with explicit metadata, then repeat resource-sensitive invariants inside the application or domain layer where background jobs and non-HTTP entry points also pass. Prefer deny-by-default behavior and test that every public and privileged route has the intended policy.
Separate customer, operator, service, deployment, and emergency identities. Use least privilege, short-lived credentials, protected secrets, auditable elevation, access review, and revocation. Model tenant isolation through authorization, query constraints, storage boundaries, cache keys, jobs, logs, exports, and support tooling; a tenant identifier in a request object is not isolation by itself.
Layer preventive, detective, and recovery controls: secure configuration, dependency and image governance, rate and concurrency limits, abuse and transaction controls, encryption and key ownership, audit evidence, privacy-aware telemetry, vulnerability management, incident response, backup restoration, and tested recovery. Give every control an owner, verification method, failure signal, exception process, and expiry. Security that cannot be observed or rehearsed will fail silently.
Set service objectives for completed business journeys before choosing scaling mechanisms. Measure p50, p95, and p99 latency by operation together with throughput, error type, queue age, pool waiting, database work, cache behavior, runtime pauses, CPU, memory, storage, network, dependency latency, and business completion. A high request rate is irrelevant if the system creates duplicates, returns stale authority, or accumulates work it cannot finish.
Profile the event loop, serialization, validation, provider scope, connection pools, query plans, indexes, payload size, N+1 access, locks, and remote call trees. Singleton providers are the normal efficient default; request-scoped dependency chains create instances per request and should solve a real context-lifetime need. Optimize only after a synchronized trace and controlled reproduction identify the causal constraint.
Keep stateless request processing horizontally scalable, but account for session state, sockets, scheduled work, local caches, rate limits, and graceful shutdown. Bound every remote call with an end-to-end deadline, shorter timeouts, cancellation, concurrency limits, safe retry rules, jitter, and circuit or degradation behavior. Retries require idempotency or a duplicate policy; otherwise overload turns uncertainty into repeated side effects.
Use queues when work can be asynchronous, peaks need buffering, or CPU-heavy work should leave request-serving processes. Define delivery guarantees, ordering scope, deduplication, retry budget, poison handling, dead-letter ownership, age limits, cancellation, replay, reconciliation, and autoscaling signals. A queue moves pressure in time; without bounded growth and consumers sized from evidence, it hides an outage.
Cache only with an explicit source of truth, key and tenant boundary, freshness promise, invalidation path, size limit, stampede protection, sensitive-data policy, and degraded behavior. Introduce separately deployable services when measured needs for ownership, isolation, scaling, or release independence repay contract versioning, network failure, distributed consistency, tracing, deployment, and on-call overhead.
A scalable NestJS backend is one whose first constraint is measurable under production demand, whose failure states are controlled, and whose boundaries let the team change one capability without destabilizing every other one.— GARNO.TECH Engineering Team
Build a risk-shaped test portfolio. Unit tests cover pure policies and transitions. Integration tests verify modules against real databases, brokers, caches, and provider contracts. Contract tests protect public and event interfaces. Focused end-to-end tests prove critical journeys, permissions, migrations, failure states, and operator repair. Load and resilience tests establish the safe operating envelope and recovery behavior. Avoid tests that merely repeat decorator or framework behavior.
Test deployment compatibility as well as code. Schema and event changes need expand-and-contract sequencing, mixed-version support, observable backfills, repair tools, and rollback or forward-fix plans. Build one traceable artifact, scan and sign it where required, promote it through environments, and retain provenance. Feature flags need an owner, safe default, telemetry, expiry, and stop condition.
Observe from the business journey down. Propagate correlation and trace context through requests, messages, jobs, database operations, and provider calls without turning telemetry into a store of sensitive data. Record structured outcomes and error classes. Alert on symptoms a team can act on: completion drops, latency objectives breach, error classes rise, saturation persists, queues age, reconciliation diverges, or a security control fails.
Health checks should describe whether an instance can accept work, not cause a dependency storm. Distinguish process liveness, readiness, critical journey health, and downstream degradation. During shutdown, stop accepting new work, drain in-flight requests and jobs within a bound, close resources, and make unfinished work recoverable. Rehearse provider loss, database pressure, queue backlog, credential rotation, bad release, restore, and required regional failure.
Choose a NestJS partner by the decisions and evidence they leave, not by framework vocabulary. A credible team begins with product journeys, domain and trust boundaries, current behavior, data ownership, integrations, service and recovery targets, delivery constraints, internal capability, and production responsibility. It names assumptions and proves the riskiest boundary before scaling implementation.
Evaluate experience across complete outcomes: authorization, transaction behavior, schema evolution, provider failure, asynchronous work, observability, secure delivery, capacity, incidents, and handover. Ask to see how architecture rules are enforced, how failures are tested, how production evidence changes a decision, and how client engineers participate. Polished diagrams without repository rules, telemetry, runbooks, and ownership do not protect the backend.
Define the engagement as a bounded result: a production feature, an architecture and security assessment, performance recovery, modernization slice, migration, platform foundation, or additional team capacity. State acceptance evidence, decision rights, access, environments, review process, dependencies, exclusions, support, and transfer. Use staged delivery when uncertainty is high, with explicit points to continue, reshape, or stop.
A partner should reduce long-term dependency. Code, infrastructure, configuration, tests, decisions, telemetry, documentation, provider access, and operational knowledge should remain visible to the client throughout delivery. The owning team must be able to build, deploy, diagnose, secure, recover, and extend the system after the engagement changes or ends.
GARNO.TECH provides NestJS development services for new products, production features, architecture improvement, integration-heavy platforms, security work, performance and reliability recovery, and incremental modernization. We connect framework mechanics to domain rules, measurable service behavior, delivery evidence, and practical ownership.
The goal is not the most elaborate NestJS structure. It is a backend whose critical transitions are correct, boundaries are enforceable, access is explicit, failures are contained, capacity is understood, changes are traceable, and recovery is rehearsed. Such a system can grow in product scope, traffic, and team size without making every release an act of faith.
@UseGuards(JwtAuthGuard, PermissionsGuard)
@RequirePermission('orders:create')
@Post()
create(
  @CurrentActor() actor: Actor,
  @Body() input: CreateOrderDto,
) {
  return this.createOrder.execute({ actor, input });
}Share the product journeys, domains, roles, data, integrations, incidents, service objectives, recovery targets, current architecture, team, and delivery constraints. GARNO.TECH can define the boundaries, production controls, evidence, and staged delivery plan.
Research and development of AI-powered solutions to optimize business workflows and enhance decision-making processes.
Analysis of machine learning models for predictive analytics in finance, e-commerce, and SaaS platforms.
Exploration of natural language processing and computer vision technologies to strengthen automation, personalization, and customer support.
Design credible MongoDB load tests with production-shaped traffic and data, end-to-end telemetry, query-plan evidence, saturation tests, recovery checks, and a defensible capacity envelope.
9 min read
Plan Azure workloads through measurable business goals, landing-zone governance, deliberate service choices, identity, security, resilience, delivery, observability, and cost ownership.
10 min read
Choose an Azure modernization strategy from workload evidence, business outcomes, data risk and operating capability, with practical guidance for rehost, replatform, refactor and rebuild.
9 min read