/ 01
Governed Foundation
Define subscriptions, identity, networking, policy, logs, tags, budgets and exceptions as versioned infrastructure before production workloads arrive.
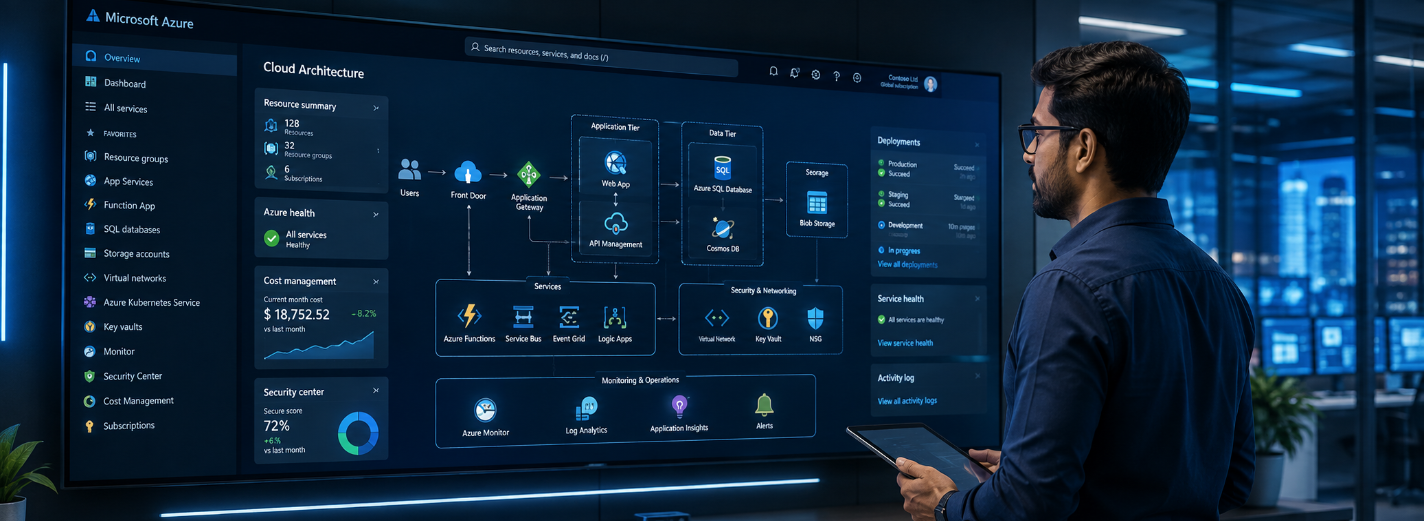
Azure cloud development should turn a product requirement into a workload the client can securely operate, recover and fund. The work may include a new SaaS product, API or data flow; modernization of an existing .NET, JavaScript or mixed estate; a migration from a data center or another cloud; or repair of a platform whose cost and reliability no longer match the business. The service begins with the customer journey, data and operating model rather than a list of Azure products.
We define users and tenants, critical workflows, identity, data classes, integrations, demand, latency and availability objectives, RTO and RPO, regions, regulatory context, release frequency, support model, budget boundary and internal capability. Those facts guide the landing zone, application boundaries, compute, data, messaging, networking, observability and delivery architecture. The five Azure Well-Architected pillars provide review coverage, while business priorities decide the trade-offs.
Every engagement has explicit ownership. Client-controlled subscriptions, repositories, domains and data avoid dependency. GARNO.TECH can own a defined outcome, work with internal engineers or provide architecture and validation. Acceptance covers product behavior, security, recovery, performance, observability, deployment and cost. A cloud resource is complete only when the receiving team can operate it.
Azure is one part of the product system. Delivery can include Angular interfaces, NestJS services, mobile clients, PostgreSQL or MongoDB data, identity, payment, reporting and third-party integrations. The architecture follows business boundaries and customer journeys so cloud components do not fragment product ownership.
Relevant experience means evidence from a similar constraint: multi-tenant authorization, regulated records, enterprise SSO, high-volume ingestion, a live migration, complex integration, strict recovery or cost pressure. We examine the initial uncertainty, options, decision, measurable outcome and lesson. A logo from the same industry is weak evidence when the proposed team did unrelated work.
Case and results blocks on this page provide context, but any quantitative claim should state its baseline, period, scope and caveats. For a new workload, we establish its own evidence through discovery and a production-shaped proof. The goal is a design that fits this organization’s product, risk and operating capacity.
Architecture starts with one production-shaped journey. We trace a request or event through edge, identity, application, authoritative data, cache, queue, external integration and background processing. We ask what happens under duplicate delivery, retry, slow dependency, partial success, a noisy tenant and regional disruption. The answers expose state, consistency, idempotency, reconciliation and operator responsibilities.
Compute follows execution behavior. Azure App Service or Container Apps can suit managed web and container workloads; Functions can suit bounded event-driven work; AKS fits teams that have a justified Kubernetes requirement and operating capability; virtual machines remain appropriate where OS control or legacy constraints demand them. Data choices follow access patterns and invariants. Azure SQL, PostgreSQL, Cosmos DB, Storage and analytical services solve different problems; “cloud-native” is not a selection criterion.
The platform foundation establishes management groups and subscriptions, Entra identity, connectivity and DNS, policy, telemetry, cost allocation and infrastructure as code. We keep application and platform ownership separate but connected. Architecture decisions record alternatives, assumptions, consequences and review triggers so the system evolves from evidence instead of fashion.
Choose a disposition for each workload from evidence. Rehosting can reduce data-center dependency quickly but usually preserves operating weaknesses. Replatforming moves selected responsibilities to managed services and needs compatibility, performance and cost proof. Refactoring or rearchitecting can improve product economics and resilience when the commercial case justifies change, but combining a redesign with a fixed migration deadline increases uncertainty. Replacement, retirement and retention are valid outcomes when ownership, value or constraints support them.
Compare options against the same criteria: business interruption, data movement, security boundary, licensing, engineering capacity, skill availability, rollback, operational burden, expected cost and time to value. Run a small technical proof for the riskiest assumption, such as database behavior, network latency, identity federation, file semantics or vendor compatibility. Avoid selecting a service because it is newer; select the simplest model that meets the workload’s targets and can be operated by the responsible team.
Turn the portfolio into waves. Start with a representative workload whose failure is survivable and whose learning can improve the landing zone. Keep tightly coupled components together, define entry and exit criteria, reserve a stabilization period and prevent several critical cutovers from sharing the same responders. Every wave needs a decision date, accountable owner, communication plan, data reconciliation and viable rollback or forward-repair path.
Security begins with a threat model and data lifecycle. Map collection, validation, transfer, storage, replication, backup, analytics, export, retention and deletion. Define tenant and object authorization, administrator paths, identity federation, secrets, keys, network exposure, audit and incident notification. A private endpoint supports network control; it does not replace application authorization.
Use Microsoft Entra groups and managed identities, least privilege, time-bounded elevation and monitored emergency access. Remove credentials from source and pipelines, rotate secrets and review guest users, service principals and role assignments. Deploy policies gradually with tests and owned exceptions. Central security findings need routing, severity, response time and evidence of closure.
Microsoft secures the Azure cloud platform while the client remains responsible for workload configuration, identities, data and application behavior according to the selected service. We write that shared-responsibility boundary down. Privacy, residency and regulated controls receive appropriate legal and specialist review; certifications support assurance but do not prove custom code, configuration or recovery.
Capacity begins with a workload model: tenant and data-size distribution, peak reads and writes, concurrency, background queues, reporting, integration quotas, retention and growth. Tests use production-shaped data and traffic to measure latency percentiles, throughput, errors, saturation and cost. We identify the next bottleneck and the threshold that triggers scaling or design change.
Reliability works backward from a customer objective. Use health signals, timeouts, bounded retries, idempotency, backpressure and graceful degradation. Availability Zones or multiple regions are justified by impact, not prestige; more redundancy adds data, release and operating complexity. Restore representative data, exercise dependencies, measure achieved RTO and RPO and let the receiving team run the recovery.
Observability links logs, metrics and traces to business journeys and releases. Alerts have an owner, urgency and repair path. Progressive delivery, feature controls or blue-green deployment limit change risk where warranted. Performance, recovery and release evidence become production gates rather than documents produced after launch.
Cloud cost is an architectural output. Model compute, database, storage, network transfer, security, telemetry, backup, support, licenses and nonproduction under normal, peak and failure demand. Connect spend to useful units such as active tenants, transactions, jobs, stored data or model calls. A cheaper resource can raise total cost when it increases engineering and incident work.
Apply allocation metadata, budgets, anomaly alerts and named owners from the foundation. Combine Azure Cost Management data with workload telemetry. Review idle resources, rightsizing, autoscaling, storage tiers and lifecycle, log retention, egress, environment schedules and commitments. Reservations or savings commitments follow a stable usage baseline; they do not replace waste removal or a sound service choice.
Optimization protects service objectives. Each proposal states the expected saving, customer and operational effect, engineering cost, validation period and rollback. Monthly cost review explains variance and unit economics, then funds changes with the best expected value. Forecasts use ranges and demand scenarios rather than a single invoice estimate.
The right Azure plan uses the fewest capabilities needed to meet measurable product, security, reliability, performance and cost objectives—and leaves a team able to operate them.— GARNO.TECH
Azure delivery crosses product, application, cloud, data, security and operations. A credible team can follow one customer journey through interface, API, identity, data, messaging, deployment and telemetry, then explain ownership and failure at every boundary. Inspect architecture records, infrastructure modules, release evidence, dashboards, restore tests and incident learning—not only certifications or service lists.
GARNO.TECH combines product engineering with Azure architecture, migration, DevOps, database work, security and operating handover. We begin with the smallest production slice that tests the expensive assumptions. Client engineers see decisions, repositories, environments and telemetry throughout delivery. Estimates change openly when evidence changes.
Continuity and exit are part of quality. Named contributors have allocation and replacement rules; documentation is tested through real tasks; accounts and artifacts remain transferable. Before completion, the client deploys a change, traces a request, responds to an alert, restores data and explains cost. The strongest provider leaves an operating capability, not permanent dependency.
Close the project against operational evidence. The receiving team should deploy a safe change, trace a representative request, explain a dashboard and alert, rotate a credential, restore data, review cost variance and execute an incident path. Confirm ownership of subscriptions, repositories, domains, data, infrastructure code, documentation and third-party agreements. Record open risks with owners and dates. A concise architecture decision log and tested runbooks are more useful than a large handover document nobody has exercised. Schedule a post-release review using customer, service and cost outcomes, then fund the next increment from what production revealed. This completion standard turns cloud delivery into an internal capability instead of a permanent dependency on the original project team.
resource vault 'Microsoft.KeyVault/vaults@2023-07-01' = {
  name: 'product-secrets'
  location: resourceGroup().location
  properties: { enableRbacAuthorization: true }
}Research and development of AI-powered solutions to optimize business workflows and enhance decision-making processes.
Analysis of machine learning models for predictive analytics in finance, e-commerce, and SaaS platforms.
Exploration of natural language processing and computer vision technologies to strengthen automation, personalization, and customer support.
Choose an Interim or Fractional CTO by the leadership gap, decision load, required authority, availability, transition plan, and evidence of outcomes.
13 min read
Learn when an Angular backend-for-frontend improves security, contracts, rendering, and delivery—and when its extra hop and ownership cost are unjustified.
10 min read
Evaluate NestJS against product complexity, team skills, security, integrations, scale, delivery pace, and operating costs before choosing it for a business backend.
9 min read