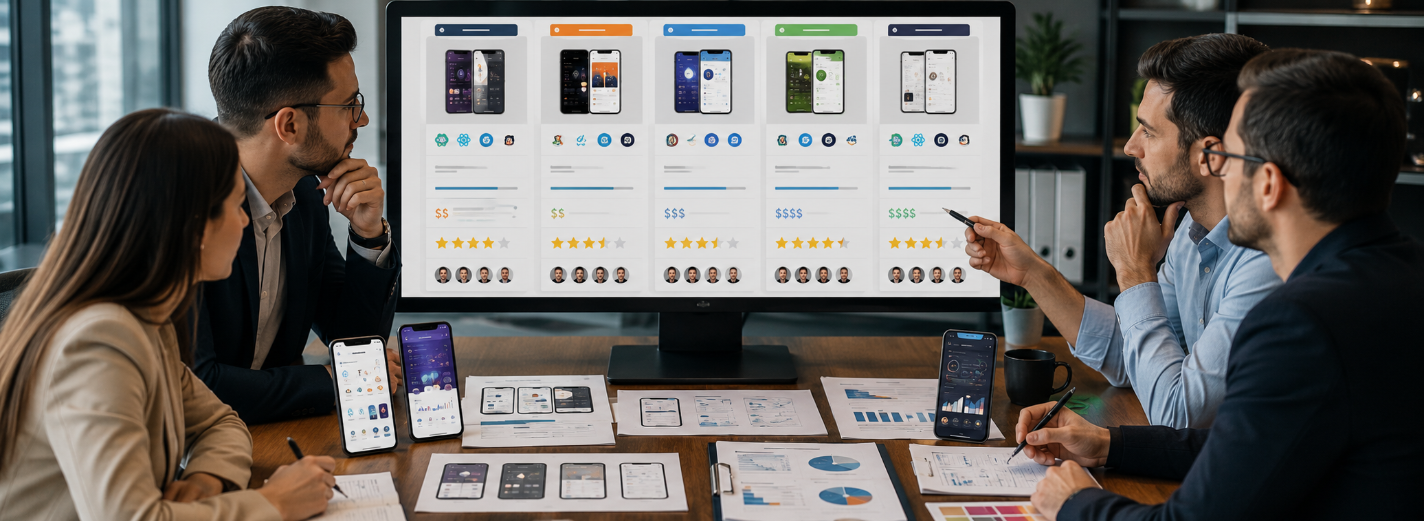
How to Choose a Mobile App Development Agency with Evidence
- mobile development
- iOS
- Android
- Flutter
- React Native
- product development
How to Choose a Mobile App Development Agency
Choosing a mobile app development agency is a product, technology, and operating decision. The team will influence what is learned before code, how the experience works across devices and poor networks, how identity and sensitive data are protected, who controls distribution accounts and signing, how quickly a failed release can be contained, and whether another team can maintain the product later.
Do not begin with a beauty contest between portfolios or hourly rates. Define the outcome and consequence, give every credible candidate the same production-shaped scenarios, and request evidence behind its claims. A polished proposal can conceal subcontracting, fragile architecture, missing quality work, client-owned tasks, or a price that stops before store release. A responsible agency makes uncertainty, exclusions, ownership, and trade-offs visible before the contract turns them into surprises.
This guide provides a due-diligence method rather than a universal ranking. Adjust security, privacy, accessibility, consumer, medical, financial, employment, and distribution obligations with qualified owners for the product and markets. Outsourcing delivery never transfers the company’s accountability to users.
Define the Product Decision Before Requesting Estimates
Write a short decision brief before asking for a fixed feature estimate. Identify the users and excluded users, the problem and current alternative, the behavior that should change, business model, launch markets, supported form factors, accessibility and language needs, sensitive data, essential device capabilities, backend and third-party integrations, offline expectations, and the metric that would justify further investment.
Describe one critical journey from entry to verified outcome, including account recovery, denied permissions, interrupted payment, expired session, no connectivity, duplicate action, background suspension, and support. Mark which assumptions are unknown. An experienced agency should challenge scope, propose a smaller evidence-producing release, and explain which uncertainties require discovery, prototype, technical spike, or real-device test.
Separate fixed constraints from negotiable scope. A regulatory date, existing backend, minimum OS, data-residency rule, brand launch, or hardware dependency may be fixed; screens and secondary features often are not. Ask candidates to estimate the same boundary with assumptions, ranges, dependencies, acceptance, and client responsibilities. Point estimates built on different hidden interpretations cannot be compared.
- Outcome and audience: define the user, unmet need, present alternative, intended behavior change, business result, success evidence, and conditions that would stop investment.
- Production boundary: list platforms, devices, markets, accessibility, languages, offline behavior, sensitive data, integrations, native capabilities, backend constraints, and operational consequence.
- First evidence slice: choose the smallest end-to-end journey that tests product demand and the most consequential UX, architecture, integration, security, or store assumption.
- Decision constraints: state budget range, target window, fixed obligations, negotiable scope, internal owners, required support, acceptance, and assumptions candidates must price consistently.
Evaluate Comparable Evidence and the Named Team
Request two or three projects similar in consequence rather than visual style. Ask what the agency actually owned, which named people performed the work, what volume and device conditions mattered, which integrations failed, how architecture changed, what escaped into production, how recovery worked, and which result was measured. A case study should distinguish evidence from marketing attribution and explain what the team would now do differently.
Domain experience matters when it reveals workflows, abuse cases, provider behavior, store policy, or regulatory evidence sooner. It becomes a liability when the agency copies another client’s solution or treats one market as universal. Engineering transfer can also be valuable: a team that has solved reliable offline synchronization in logistics may understand a field-health workflow better than an agency with one attractive medical landing page.
Meet the people proposed for discovery, product, UX, mobile architecture, backend, quality, security, delivery, and release—not only sales leadership. Verify availability, seniority, location and time overlap, language, employment or subcontracting, substitution rights, and who makes decisions when disciplines disagree. Ask each lead to reason through one difficult scenario using incomplete information. Specific questions and acknowledged limits are stronger evidence than instant certainty.
Inspect a sanitized architecture decision, risk or assumption log, test strategy, pull request, CI/CD flow, release checklist, crash investigation, and handover artifact. Ask references about a changed estimate, missed milestone, production incident, team replacement, unpopular trade-off, and exit. A trustworthy agency protects other clients’ source, vulnerabilities, credentials, and personal data; refusal to expose confidential material is a positive signal when it offers safe alternative evidence.
Test Native and Cross-Platform Recommendations
Ask the agency to compare at least two viable approaches against the brief. Native Swift and Kotlin development provides direct platform APIs, early access to new capabilities, granular performance control, and platform-specific interaction. It usually requires parallel implementation and expertise. React Native, Flutter, Kotlin Multiplatform, shared business modules, or another cross-platform model can reduce duplication, but the actual saving depends on UI, native integrations, release cadence, package quality, debugging, and how much platform-specific code remains.
Test the recommendation with concrete constraints: camera and media pipelines, Bluetooth or NFC, maps, background work, push, widgets, biometrics, payments, accessibility, animations, startup, memory, battery, offline data, deep links, analytics, crash reporting, and supported OS versions. Ask what remains shared, how native escape hatches work, who maintains bridges and plugins, and what happens when Apple or Google changes a platform API. A framework demo on one recent device does not prove production fit.
Architecture should also cover backend contracts, identity, authorization, local storage, synchronization, conflict resolution, migrations, feature controls, telemetry, and compatibility with older app versions that cannot be forced to update. Require performance and accessibility budgets, dependency policy, and a thin vertical proof for the highest-risk capability. The right answer can be native, cross-platform, hybrid, or mobile web; the evidence should choose it.
A trustworthy mobile agency does not sell its preferred framework as the answer. It exposes product assumptions, compares viable architectures, proves the risky path, and protects the client’s ability to operate and leave.— GARNO.TECH Product Team
Inspect How the Agency Discovers, Delivers, and Releases
Discovery should produce decisions: validated users and journeys, prototype evidence, domain and data model, system boundary, risk and threat model, architecture options, release plan, measurement, assumptions, and a prioritized first slice. Ask who owns product choices and who signs off behavior, design, security, and release. A backlog of untested requests is not discovery.
Delivery should expose completed, testable outcomes at a useful cadence. Inspect how the team plans, reviews design, branches and reviews code, controls dependencies, tests, demonstrates real builds, reports risk, handles scope change, and forecasts. You should have client-controlled access to the tracker, repositories, design source, environments, build results, decisions, and telemetry from the beginning. Status should distinguish done, blocked, uncertain, and accepted rather than translate activity into an optimistic percentage.
Release engineering is part of the product. Verify reproducible builds, environment configuration, secrets, signing, build provenance, beta tracks, store metadata, privacy disclosures, review lead time, phased or staged rollout, feature controls, crash and performance monitoring, rollback or hotfix, and authority to pause. Test on representative physical devices and network conditions. A mobile binary cannot always be rolled back instantly after store distribution, so server compatibility and remote containment matter.
Compare Total Cost, Control, and Ownership
Compare proposals on the same cost boundary. Separate discovery, research, design, mobile and backend development, integrations, data migration, analytics, quality, security assessment, accessibility, devices and services, CI/CD, cloud, developer programmes, store preparation, launch, warranty, support, maintenance, taxes, and contingency. Identify third-party fees and client work. Model at least launch plus an operating period; the cheapest build can become the most expensive product when updates and incidents are excluded.
Understand the commercial mechanism—fixed scope, time and materials, capacity, milestone, retainer, or hybrid—and the risk it assigns. Define estimate confidence, staffing, billing unit, acceptance, defect, change, delay, pause, cancellation, warranty, emergency work, and payment. Preserve a decision point after discovery or a vertical slice. Paying for evidence that stops a weak product is better than using contract momentum to finish it.
The client organization should own the Apple and Google developer accounts, app records, bundle and package identifiers, domains, cloud and backend accounts, source and design repositories, data, analytics, push configuration, third-party contracts, and distribution authority. Apple’s Account Holder carries unique legal and membership powers; Google Play signing distinguishes the protected app-signing key from the upload key. Give the agency role-based access. Define intellectual property, prior materials, open-source obligations, credentials, export formats, portfolio use, retention, deletion, handover, and the right to appoint another team.
Verify Security, Quality, and Product Operations
Ask for a threat model tied to the actual assets, actors, trust boundaries, and abuse cases. Mobile controls should address local storage and logs, cryptography and keys, authentication and server-side authorization, network communication, platform interaction, WebViews and deep links, permissions, update integrity, dependency risk, tampering where relevant, and privacy. OWASP MASVS offers a useful verification structure, but the product’s risk determines depth. A claim that HTTPS or store review makes the app secure is disqualifying.
Map tests to consequence: unit and component behavior, API contracts, integration, critical journeys, accessibility, localization, permissions, interrupted and slow networks, offline recovery, background transitions, device and OS matrix, installation and upgrade, corrupted local state, performance, battery, memory, security, analytics, release configuration, and backend compatibility. Define severity, evidence, release gates, flaky-test ownership, independent assessment where warranted, and production validation. Counting test cases without risk coverage is weak assurance.
Request the operating model before launch. It should name service objectives, dashboards and alerts, crash triage, app-review and policy ownership, customer support escalation, incident roles, vulnerability and dependency updates, supported OS policy, certificate and key rotation, backup restoration for backend data, analytics and experiment review, cost, on-call coverage, and store release authority. Distinguish warranty, maintenance, support, feature work, and emergency response.
Test continuity: can the client build and sign from a clean environment, release to test tracks, reach production telemetry, recover critical access, restore backend data, replace a team member, and operate from the documentation? Require a transition plan and periodic knowledge transfer. A long support contract is not continuity when the vendor alone controls accounts, keys, pipelines, or undocumented knowledge.
Make the Decision with a Scorecard and a Proof
Score every candidate against the same weighted model: product understanding, named team, comparable evidence, UX and accessibility, mobile and backend architecture, security and privacy, quality, delivery and release, communication, ownership and exit, operating support, price clarity, and concentration risk. Mark mandatory conditions separately. Include internal effort and the cost of delay rather than ranking only supplier fees.
Use a paid discovery or production-shaped vertical proof when proposals cannot resolve the highest-risk uncertainty. Define the question, time box, deliverables, access, acceptance, ownership, and stopping rule. Judge how the agency learns, reports bad news, documents decisions, handles failure, and leaves reusable evidence—not how much code it produces in the time.
Contract material claims as named roles, scope, acceptance, security duties, incident cooperation, accounts, intellectual property, subcontracting, service levels, evidence, change control, data return, termination, transition, and deletion. Keep an accountable internal product and technology owner. The best agency is the one whose decisions remain understandable, whose controls are verifiable, and whose work increases the client’s ability to operate and change the product after the first release.
A Four-Step Mobile Agency Assessment
- /01Define the Product and Operating BoundaryMap users, outcomes, journeys, devices, markets, accessibility, data, native capabilities, integrations, offline behavior, store constraints, support, fixed obligations, and the evidence required to proceed.
- /02Inspect the Named Team and Its EvidenceGive candidates the same difficult scenarios; review comparable work, decision records, technical artifacts, security and test reasoning, incidents, references, staffing, subcontracting, and acknowledged limits.
- /03Prove Delivery and Release on a Vertical SliceExercise one real journey through design, app, API, data, telemetry, physical devices, slow and interrupted networks, automated build, signing, test distribution, failure containment, support, and acceptance.
- /04Contract Control, Operations, and ExitPut accounts, source, designs, data, artifacts, named roles, security, quality, acceptance, support, costs, change, incident cooperation, knowledge transfer, termination, data return, and transition into the agreement.
What evidence should decide which mobile app development agency to hire?
What evidence should decide which mobile app development agency to hire?
Turn Agency Selection into a Defensible Product Decision
Share the product outcome, users, critical journey, markets, device capabilities, integrations, sensitive data, current architecture, budget boundary, deadline, candidate proposals, and internal owners. GARNO.TECH can define an evidence request, weighted scorecard, technical scenarios, production-shaped proof, risk register, acceptance, account ownership, operating model, and transition criteria.
Publications
Our research
Research and development of AI-powered solutions to optimize business workflows and enhance decision-making processes.
Analysis of machine learning models for predictive analytics in finance, e-commerce, and SaaS platforms.
Exploration of natural language processing and computer vision technologies to strengthen automation, personalization, and customer support.
Modular Monolith with NestJS: A Practical Architecture Guide
Design a NestJS modular monolith with business boundaries, small public APIs, owned data, local transactions, reliable events, enforceable dependencies, and an evidence-based path to service extraction.
8 min read
08 Sep 2026
Scaling Angular Applications as Products and Teams Grow
Scale an Angular product through domain boundaries, deliberate state, performance evidence, accessible design, safe delivery, and routine modernization.
9 min read
04 Aug 2026
Angular Application Modernization: Audit Before You Rewrite
A production guide to auditing an Angular application before modernization: dependency health, architecture boundaries, performance, security, tests, build pipeline, UI debt, staged upgrades and rewrite decisions.
10 min read
28 Aug 2026