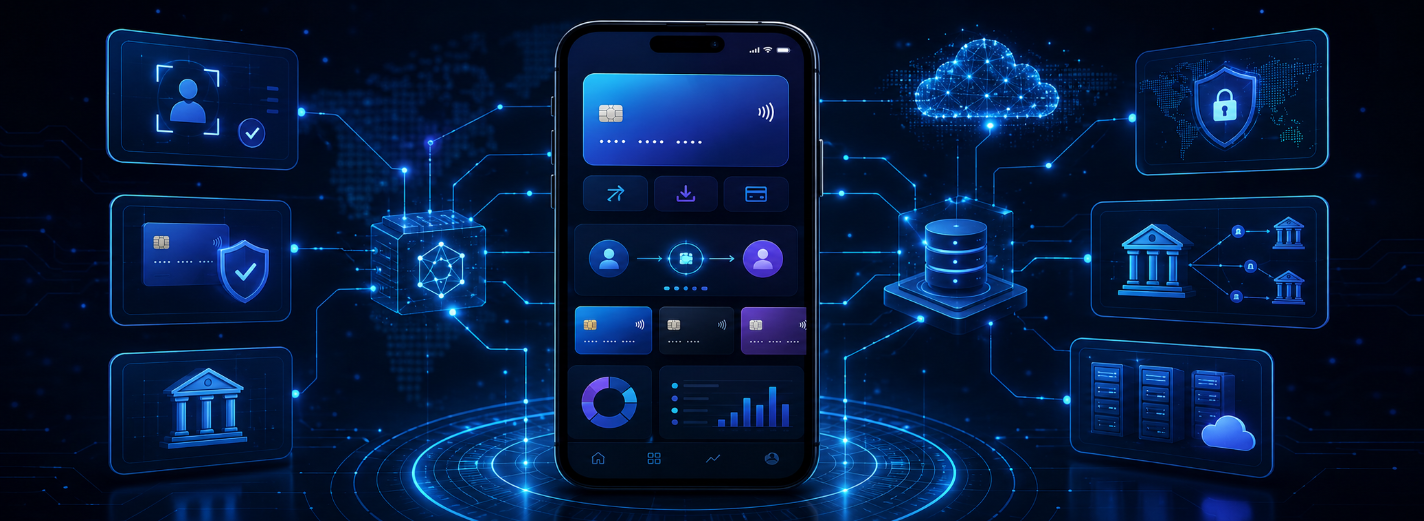
/ 01
Complete Transaction Model
Estimate authorization, pending and failed states, reversals, disputes, reconciliation, evidence, communications, and operator repair together with the initiating feature.
Asking “How much does a FinTech app cost?” is useful only after the word app has been replaced by an operating system of responsibilities. A clean interface may sit above identity checks, money movement, provider certification, ledger evidence, permissions, reconciliation, disputes, reporting, support, incident response, and recovery. Two products with the same number of screens can differ by an order of magnitude in risk and ownership.
A credible estimate is therefore a range tied to a defined result, assumptions, exclusions, confidence, and date. It states the entity and markets, users and operators, transaction lifecycle, regulated boundary, providers, service targets, launch route, team, internal responsibilities, third-party charges, contingency, and operating period. It also states which missing facts can materially change the range.
The aim is not to predict every hour before learning begins. It is to make uncertainty visible enough to fund the next decision, compare delivery options, detect variance early, and stop an uneconomic direction before sunk cost becomes an argument for continuing. A budget becomes governable when every major amount has a reason, owner, evidence requirement, and rule for reforecasting.
Begin with a one-page estimation boundary. Name the customer outcome, business model, countries, legal entities, channels, user and operator roles, financial products, currencies, transaction volume, data sensitivity, providers, availability and recovery targets, target date, and capabilities already owned. Separate the first launch from future options. “Multi-country,” “all payment methods,” and “enterprise-ready” are ambitions, not estimable requirements.
Decompose the result into work streams: product discovery, experience and content, financial domain design, application and data engineering, provider integration, security and privacy, regulatory evidence, quality engineering, environments and delivery, migration, launch, training, support, and operation. Include the client work that sits outside a supplier invoice—legal interpretation, policy decisions, provider contracts, access to subject-matter experts, data preparation, acceptance, and operational staffing.
For each work package record scope, dependencies, owner, acceptance evidence, low/expected/high effort, pass-through cost, uncertainty, and the fact that would narrow it. Do not add every pessimistic number; model correlated risks and hold a transparent management reserve. Keep contingency separate from scope so it cannot quietly finance new features. Display tax, currency, rate date, inflation assumption, payment schedule, and whether fees are one-time, monthly, per-user, per-check, or per-transaction.
A feature name hides the states that create cost. “Transfer money” may require creation, eligibility, authorization, strong authentication, submission, pending, partial success, rejection, expiry, duplicate suppression, reversal, refund, dispute, reconciliation, correction, and customer notification. Each state affects the data model, API, interface, permissions, evidence, monitoring, support tooling, and tests.
Map one representative transaction from intent to settlement and repair. Identify the authoritative record, amount and currency rules, balance treatment, fees, limits, ordering, idempotency, timestamps, provider callbacks, late and contradictory events, manual interventions, and immutable audit evidence. Estimate the happy path only after the exceptional paths and operator actions are visible. Financial software often spends more effort proving and repairing a transaction than drawing its initiating screen.
Apply the same method to identity verification, onboarding, lending, cards, investment, insurance, open banking, or digital assets. Price the decision lifecycle, provider behavior, consent and retention, false positives, appeals, statements, reporting, and offboarding. Remove optional lifecycles from the first boundary rather than leaving them as vague “minor additions.” A smaller coherent product is easier to estimate and safer to fund than a broad MVP with financially ambiguous edges.
Security and compliance costs come from defining controls, implementing them, producing evidence, and operating them. Budget data classification, threat modeling, identity and authorization, privileged access, encryption and key ownership, secrets, secure delivery, dependency management, audit records, fraud and transaction controls, monitoring, vulnerability testing, incident response, backup restoration, resilience exercises, remediation, documentation, and training.
Determine obligations from the entity, activity, role, market, customer, data, payment flow, outsourcing chain, and provider contracts. A regulated provider can perform a licensed or certified capability without transferring every responsibility. Record who decides, who performs, who supplies evidence, who monitors, and who responds when the control fails. Separate legal advice, licences, external audits, certification, insurance, and regulator or scheme fees from software delivery while keeping them on the same launch plan.
Estimate evidence alongside functionality. Acceptance may require access reviews, architecture and threat records, data-flow maps, test results, traceable approvals, audit retention, provider due diligence, recovery proof, operating procedures, staff training, and a remediation window. Postponing this work does not remove it; it moves discovery toward the launch date, when redesign, contract change, and delay are most expensive.
A useful FinTech estimate does not hide uncertainty. It prices what is known, reserves for what is not, and defines the evidence that will narrow the next decision.— GARNO.TECH Engineering Team
Build the team from capabilities, not titles alone. Product and domain leadership define outcomes and financial behavior. Design covers customer, support, risk, and administrator journeys. Engineers own applications, data, integrations, and platform work. Quality engineering covers contracts, state transitions, browsers, performance, security, and recovery. Security, privacy, compliance, finance, operations, support, and legal owners contribute decisions and evidence even when they are not full-time project members.
Show allocation and availability by phase. A nominal ten-person team does not provide ten people of throughput when specialists split across projects, decisions wait for the client, or onboarding consumes senior capacity. Include ramp-up, leave, time-zone overlap, review bottlenecks, environments, provider support windows, and the cost of coordinating parallel streams. Adding developers cannot compress a schedule controlled by certification, data migration, a banking contract, or one overloaded decision owner.
Build a dependency network rather than converting effort directly into a date. Mark provider onboarding, legal interpretation, procurement, credentials, sandbox quality, certification, test data, design decisions, app-store review, migration rehearsals, security assessment, training, and launch approval. Give each external dependency an owner, requested date, latest safe date, fallback, and escalation path.
Use ranges for both effort and elapsed time. A task may require five engineering days but wait six weeks for an external approval. Run a production-shaped slice early through the riskiest provider, transaction, permission, and deployment path. Replace assumptions with observed throughput and reforecast after discovery, the slice, provider approval, scope acceptance, and launch readiness. A deadline is credible when the critical path, decision latency, and schedule reserve are visible.
Fixed price works for a tightly bounded discovery, assessment, or migration with stable inputs and objective acceptance. Time and materials fits product work whose priorities will change as customer, provider, and regulatory evidence arrives. A capped team, milestone funding, or target-cost model can add spending boundaries without pretending uncertainty has disappeared. The label matters less than the rules beneath it.
Define deliverables, acceptance evidence, estimate assumptions, client inputs, change control, defect treatment, third-party delays, intellectual property, subcontracting, security duties, environments, pause and termination, handover, and the treatment of unused or exhausted contingency. Link payment to reviewable outcomes where possible. A low fixed bid can hide reduced assurance, narrow exclusions, optimistic dependencies, or future change requests rather than genuine efficiency.
Compare proposals on the same scenario. Normalize roles, allocation, seniority, productive hours, location, taxes, travel, provider and cloud fees, security work, launch support, warranty, ongoing ownership, and internal effort. Ask each bidder to show what breaks the estimate and what evidence would move it down as well as up. A proposal is more useful when it exposes its uncertainty than when it offers the most confident single number.
Approve the budget in gates. A discovery gate should resolve business, transaction, provider, regulatory, architecture, and operating assumptions. A representative slice should prove the riskiest end-to-end path. A first-release gate should define production controls and launch evidence. Scale funding should follow measured demand, provider behavior, control performance, operational load, and team throughput. Each gate needs a spending limit, decision date, evidence, and stop or reshape option.
Maintain an assumptions and decisions ledger. At each review compare actual spend, completed evidence, remaining work, dependency movement, defects, incidents, operational learning, and forecast at completion. Explain variance by cause—scope, rate, productivity, rework, delay, external fee, or realized risk—rather than hiding it in percent complete. Reforecast when evidence changes; preserving an obsolete baseline creates late surprises, not discipline.
Model total ownership cost before build approval. Include cloud environments, storage and transfer, logs and retention, identity checks, payment and banking fees, messaging, fraud tooling, licences, certificates, app stores, observability, support systems, insurance, audits, and external advice. Express variable cost per active customer, verification, transaction, dispute, report, and support case under expected and stress volumes.
Fund the operating team: support, reconciliation, financial operations, on-call response, access review, vulnerability remediation, dependency upgrades, provider changes, recovery tests, cost management, regulatory updates, data requests, and product improvement. Include lifecycle events such as a new market, provider replacement, migration, major incident, acquisition, or orderly shutdown. A product that fits the build budget can still fail its unit economics or operating capacity.
A responsible FinTech estimate is a decision model, not a promise that uncertainty has vanished. It connects money to a bounded product outcome, complete transaction behavior, evidence, dependencies, team capacity, launch, and operation. It can explain why the range changed and whether the next unit of spending removes a meaningful risk or creates measurable value.
Begin by funding the smallest investigation that can change the investment decision. Test the hardest provider boundary, financial rule, authorization model, migration, or operational exception before scaling the team. Then fund a coherent release with explicit acceptance and stop conditions. This approach may produce a less impressive number on day one, but it gives leadership something more valuable: a budget that can be challenged, compared, governed, and revised before the product runs out of time or trust.
Share the markets, transaction journey, providers, obligations, launch target, available team, operating model, existing evidence, and unresolved decisions. GARNO.TECH can build the estimation boundary, dependency map, confidence ranges, acceptance gates, ownership model, contingency, and total-cost forecast.
Research and development of AI-powered solutions to optimize business workflows and enhance decision-making processes.
Analysis of machine learning models for predictive analytics in finance, e-commerce, and SaaS platforms.
Exploration of natural language processing and computer vision technologies to strengthen automation, personalization, and customer support.
A practical decision guide to NestJS modules, dependency injection, TypeScript boundaries, modular monoliths, transports, security, testing, cloud operations, and framework fit.
9 min read
Choose a technology leadership model from decision load, executive accountability, availability, people management, company complexity, economics, risk, transition triggers, and measurable outcomes.
9 min read
Design an Azure landing zone around workload ownership, management groups, subscriptions, identity, networking, policy, telemetry, cost and automated onboarding.
9 min read