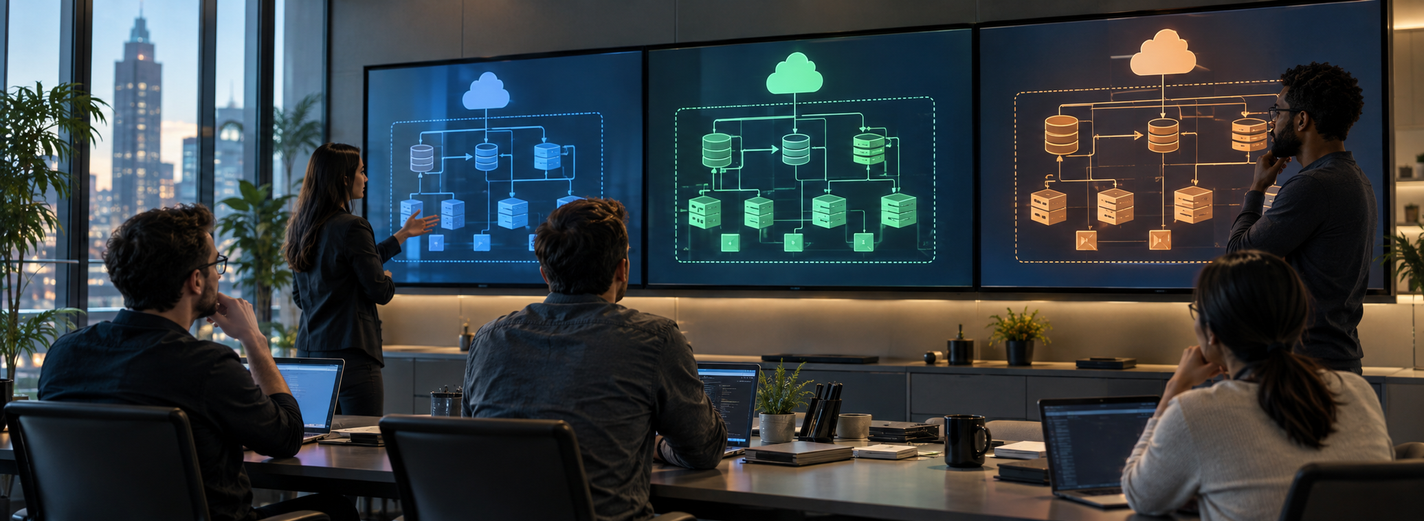
NestJS Multi-Tenant SaaS Architecture: A Production Guide
- NestJS multi tenant architecture
- nestjs
- architecture
- development
Multi-tenancy is a trust model that affects every path through a SaaS product. A tenant identifier in one database table is insufficient. Tenant context must be derived from a trusted boundary and preserved through HTTP and GraphQL requests, WebSockets, queues, scheduled jobs, caches, files, search, analytics, logs, billing, exports, support tools, backups, and recovery. One missing path can expose another customer’s data or apply the wrong commercial rule.
Begin with product and risk evidence: who a tenant represents; whether users can belong to several tenants; which resources, identities, plans, keys, regions, and retention rules vary; regulatory and contractual isolation; largest-tenant distribution; customization; noisy-neighbour tolerance; restore and deletion requirements; and the team that will operate the platform. Then choose data and compute boundaries. NestJS dependency injection can carry scoped services, but application scope alone does not establish trust.
This guide treats shared, partitioned, isolated, and hybrid models as deliberate trade-offs. The production design must explain identification, authorization, data access, background work, configuration, billing, migrations, observability, incident response, and movement between tiers. The best model is the least complex one that satisfies real isolation and operational requirements while remaining testable.
Choose the Tenancy Model from Isolation and Operations
A shared application and shared schema usually offers the lowest infrastructure and migration cost. Every tenant-owned row carries an immutable tenant key, and every unique constraint, index, relationship, and query respects it. This fits many products when logical isolation is acceptable and controls are difficult to bypass. Its greatest risk is broad blast radius from a missing predicate, unsafe cache key, or unscoped administrative query.
Shared compute with separate schemas or databases increases isolation, per-tenant backup and restore options, and customization, but multiplies connection management, schema migrations, monitoring, capacity planning, and fleet operations. Dedicated stacks can satisfy stronger regulatory, regional, key, performance, or contractual boundaries at the highest operating cost. A hybrid model may place most tenants in a shared tier and selected tenants in isolated cells.
Choose against concrete scenarios: cross-tenant read, privileged support, a large tenant exhausting capacity, regional restriction, per-tenant restore, encryption-key separation, schema rollout across thousands of databases, data export and deletion, and movement from shared to isolated. Record which boundary is enforced by application code, database policy, account or subscription, network, key, or physical deployment—and who verifies it.
Shared, Partitioned, or Isolated Data
Shared data needs composite design. Primary and foreign references, natural uniqueness, indexes, and conflict handling include the tenant boundary where appropriate; an email or external identifier may be unique within a tenant rather than globally. Repository interfaces accept tenant context explicitly and return tenant-scoped types. Raw queries, reporting, imports, maintenance scripts, and migrations follow the same rule.
Database row-level security can provide defence in depth when the chosen database and connection model support it, but only if transaction-scoped context is set and reliably cleared. Connection pools make leaked session state dangerous. Separate databases need a registry, safe credential retrieval, bounded pools, health and version tracking, migration orchestration, backup policy, and protection against a single request creating unbounded connections.
Test isolation as an invariant. Generate records with identical identifiers for multiple tenants; exercise reads, updates, deletes, aggregates, search, pagination, relations, caches, jobs, exports, logs, and administrative paths; verify negative authorization and concurrency. Backups need representative restore and reconciliation at the promised boundary. Custom NestJS development can turn the selected model into bounded implementation and migration work.
Establish Tenant Context at a Trusted Boundary
Tenant identity may arrive through a verified custom domain, subdomain, route, selected organization, API credential, or signed token claim. Treat host names, headers, and route values as hints until they are matched to authenticated membership and an active tenant in a trusted registry. Never let a caller assert an arbitrary tenant ID that downstream code accepts unchanged.
Create one immutable request context after authentication and membership checks. It can contain tenant ID, user or service principal, membership, request and correlation IDs, policy-relevant attributes, and support-impersonation evidence. Make it available through an explicit application boundary or carefully governed async context. Avoid request-scoped dependency graphs for every provider when they add allocation and testing cost without improving isolation.
Every boundary establishes context anew. Queue messages and scheduled jobs include a signed or trusted tenant reference and immutable business identifiers; consumers validate them and never inherit ambient HTTP state. WebSocket connections revalidate membership as sessions and roles change. Logs, traces, metrics, cache keys, file paths, search indexes, and outbound requests carry a safe tenant dimension without exposing sensitive values.
Separate Authentication from Tenant Authorization
Authentication proves a principal; authorization decides whether that principal may perform this action on this resource for this tenant now. A valid token with a tenant claim is not sufficient. Verify issuer, audience, signature, lifetime, revocation or session policy, membership state, selected tenant, role or attributes, entitlement, resource ownership, and action-specific conditions at the server boundary.
Keep policy close to domain operations. NestJS guards can reject unauthenticated requests and establish coarse route requirements, but resource authorization often needs loaded state and belongs in an application policy or command handler. Default to deny. Avoid scattered role strings and controller-only checks that background jobs, GraphQL resolvers, internal calls, or new transports can bypass.
Model invitations, membership changes, offboarding, service accounts, API keys, administrator roles, and break-glass support explicitly. Privileged impersonation needs approval, purpose, time limit, visible banner, tamper-evident audit, and a path that cannot reveal credentials. Test horizontal and vertical privilege escalation, stale tokens, removed memberships, tenant switching, identifier guessing, bulk actions, and exports.
Make Data Isolation the Default Path
Isolation should be difficult to forget. Put tenant-scoped repositories and storage adapters behind interfaces that require context; generate cache and idempotency keys through approved helpers; create file and search namespaces centrally; and lint or architecture-test forbidden access paths. Avoid global “current tenant” variables and optional tenant parameters whose absence broadens a query.
Analytics and operations deserve the same discipline. Cross-tenant reporting uses a separate authorized path, purpose, data model, and audit trail rather than disabling normal filters. Logs avoid payloads and secrets, while tenant dimensions follow privacy and cardinality rules. Non-production environments use synthetic or properly protected data. Support exports and deletion cover derived stores, files, search, analytics, queues, backups, and vendor copies according to the agreed lifecycle.
Assume a control will eventually fail and layer protections: application scoping, database constraints or policies, isolated credentials, encryption keys where required, network and account boundaries, anomaly detection, and audit evidence. Incident runbooks must identify affected tenants, contain access, preserve evidence, communicate according to obligations, reconcile data, and verify recovery without widening exposure.
Carry Tenant Semantics into Jobs, Billing, and Configuration
Background jobs are tenant operations without an HTTP request. Enqueue a tenant reference, immutable operation ID, actor or system purpose, and versioned payload; validate context on consumption; make effects idempotent; bound retries; isolate dead letters; and preserve correlation. Fair scheduling, per-tenant concurrency, quotas, and backpressure stop one customer’s import or report from starving the fleet.
Keep plans, entitlements, usage, and billing separate. Entitlements answer what a tenant may use now; billing records commercial events and money. Model effective dates, trials, upgrades, downgrades, cancellation, grace periods, provider webhooks, invoices, credits, refunds, and reconciliation. Duplicate or delayed provider events must not grant twice, revoke prematurely, or leave access permanently inconsistent.
Tenant configuration needs schema, validation, defaults, version, provenance, audit, rollout, and safe caching. Feature flags are temporary exposure controls, not a substitute for entitlements or permanent forks. Secrets belong in secret management and are referenced, rotated, and scoped. Configuration changes that alter data, billing, or security need preview, approval, and recovery like code changes.
Scale Tenant Operations, Not Only Requests
Measure distribution, not only totals: active tenants, records and storage per tenant, request and job rate, latency, errors, queue age, connections, cache use, provider calls, support load, and unit cost. Protect critical shared resources with quotas, admission control, per-tenant concurrency, workload classes, timeouts, and degraded modes. Promote exceptional tenants to a different cell when evidence justifies the operational boundary.
Schema and application changes become fleet operations. Keep releases backward and forward compatible while versions coexist; use expand-migrate-contract; track every database or cell by version; canary small cohorts; pause on defined health or reconciliation failures; and roll forward when data change makes binary rollback unsafe. Avoid tenant-specific code branches that prevent common upgrades.
Observability needs both fleet and tenant views. High-cardinality tenant IDs may not belong on every metric, so combine bounded metrics with searchable logs, traces, exemplars, and targeted per-tenant telemetry. Define service objectives for critical journeys, alerts with owners, incident segmentation, backup and restore evidence, capacity forecasts, and cost allocation. Scaling succeeds when operations remain explainable as tenant count grows.
When External Architecture and Delivery Capacity Helps
External review is useful when a tenancy change crosses application code, databases, identity, queues, cloud boundaries, billing, and support; when an enterprise contract introduces isolation or residency requirements; when cross-tenant risk is uncertain; or when a shared model must evolve without downtime. The review should use real journeys, schema and queries, authorization paths, jobs, infrastructure, telemetry, incidents, and operating constraints.
A useful outcome is a decision package: threat and tenant-boundary map, viable models and rejected alternatives, migration and coexistence sequence, data reconciliation, representative tests, acceptance and stop thresholds, observability, rollback or roll-forward, ownership, cost, and knowledge transfer. Implementation can then proceed in bounded slices. External expertise creates value when internal engineers can operate and evolve the result without permanent dependence.
- Choose the trust boundary: define the tenant, membership model, regulatory and contractual isolation, customization, noisy-neighbour tolerance, restore, deletion, residency, largest-tenant distribution, and operating owner.
- Design data ownership: select shared, partitioned, isolated, or hybrid storage; scope keys, constraints, indexes, repositories, backups, migrations, and reconciliation to that boundary.
- Establish trusted context: derive tenant identity from verified host, token, credential, or membership; create immutable context and revalidate it at queues, jobs, sockets, and integrations.
- Authorize the resource and action: verify membership, role or attributes, entitlement, resource ownership, current state, and support privilege on the server; default to deny and audit elevated access.
- Test isolation end to end: cover identical IDs, queries, relations, caches, files, search, analytics, logs, jobs, exports, administration, concurrency, restore, deletion, and incident containment.
- Operate the fleet: govern jobs, entitlements, billing, configuration, quotas, schema versions, canaries, telemetry, service objectives, recovery, capacity, cost, and movement between tenancy tiers.
Which NestJS multi-tenant model should we choose?
Which NestJS multi-tenant model should we choose?
Is a database per tenant more secure?
Is a database per tenant more secure?
Should NestJS use request-scoped providers for tenant context?
Should NestJS use request-scoped providers for tenant context?
How do we prevent cross-tenant access?
How do we prevent cross-tenant access?
How can a SaaS platform move a tenant to an isolated tier?
How can a SaaS platform move a tenant to an isolated tier?
Design Multi-Tenancy as a Verifiable Trust Boundary
Share the tenant and membership model, critical journeys, data stores, identity and authorization, jobs, billing, integrations, isolation obligations, tenant distribution, service targets, incidents, and expected growth. GARNO.TECH will compare viable models and define a migration-ready architecture with tests, acceptance, ownership, operations, and rollback.
Publications
Our research
Research and development of AI-powered solutions to optimize business workflows and enhance decision-making processes.
Analysis of machine learning models for predictive analytics in finance, e-commerce, and SaaS platforms.
Exploration of natural language processing and computer vision technologies to strengthen automation, personalization, and customer support.
NestJS for Business Applications: Architecture, Benefits, and Trade-offs
A practical decision guide to NestJS modules, dependency injection, TypeScript boundaries, modular monoliths, transports, security, testing, cloud operations, and framework fit.
9 min read
01 Aug 2026
Azure Database Migration: Assessment, Cutover, and Rollback
Plan an Azure database migration through workload assessment, target selection, compatibility remediation, data movement, integrity checks, cutover, rollback, and optimization.
10 min read
10 Sep 2026
Azure Cost Optimization After Migration: A Production Guide
Reduce Azure spend through workload evidence, rightsizing, autoscaling, commitments, data lifecycle, telemetry controls, Kubernetes economics and accountable FinOps.
11 min read
23 Aug 2026