FinTech Solutions: Architecture for Payments, Wallets, and Financial Operations
- FinTech solutions
- FinTech development
- payment platforms
- digital wallets
- financial software
- KYC AML
- ledger systems
- banking integrations
- financial APIs
A FinTech solution is not a polished interface wrapped around a payment API. It is an operating system for financial promises: who may move value, which institution performs the movement, when the result becomes final, how balances are explained, what happens when providers disagree, and which evidence lets customers and operators trust the answer.
Products vary widely—payment orchestration, merchant platforms, wallets, embedded finance, lending workflows, treasury tools, investment operations, billing, or financial reporting—but the design method is consistent. Trace the value flow from intent through authorization, execution, settlement, refund, reversal, dispute, and reconciliation. Name every actor, jurisdiction, currency, provider, authoritative record, timing expectation, exception, and customer-visible state.
That map separates product responsibility from regulated and provider responsibility. A bank or processor may hold funds; an identity service may return verification evidence; the application still owns its promises, state transitions, permissions, support experience, and record of what occurred. Vendor APIs should be treated as fallible external systems whose delays, duplicates, outages, breaking changes, and exit constraints are part of the product.
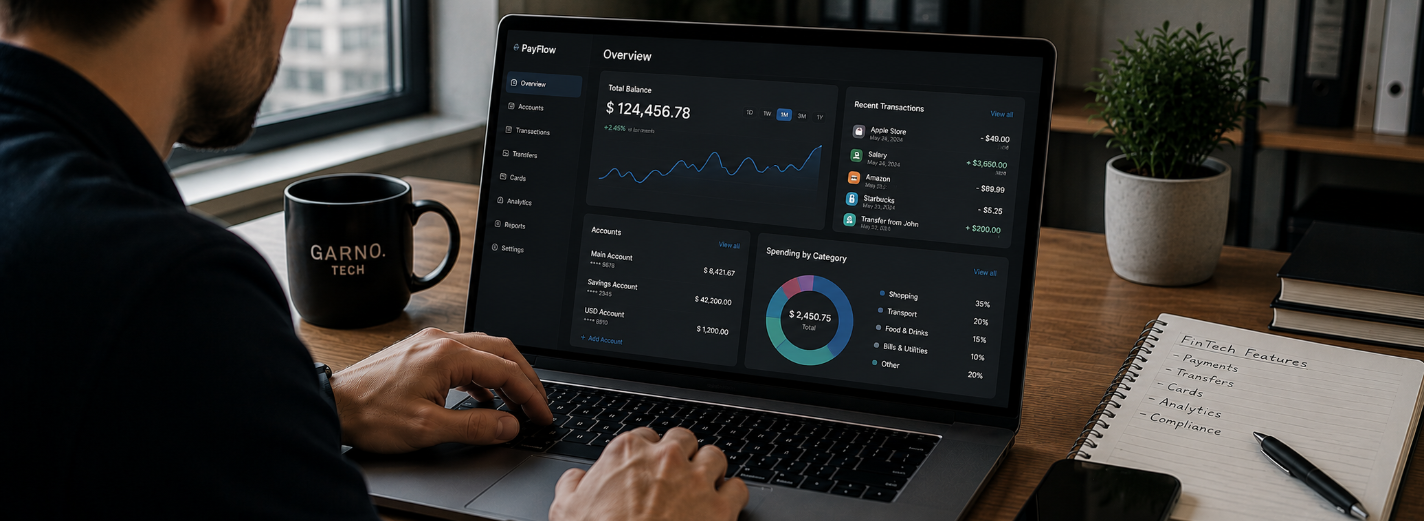
GARNO.TECH designs custom FinTech software around these flows. We connect product discovery, domain architecture, interfaces, backend services, cloud infrastructure, QA, and operations so that a launch is usable, explainable, and supportable—not merely feature complete.
What a Modern FinTech Solution Must Include
The customer layer covers onboarding, authentication, accounts, beneficiaries, payment initiation, transfers, cards or bank-payment methods, fees, exchange, payouts, refunds, disputes, statements, notifications, and consent. Each screen needs honest status language. “Submitted,” “accepted,” “pending,” and “settled” are different facts; displaying success too early creates customer and support risk.
Identity workflows include KYC or KYB data collection, document handling, provider checks, case states, expiry, resubmission, manual review, enhanced due diligence, restrictions, and decision history. Software should implement the policy defined by the client, licensed entities, and qualified advisers while preserving evidence of the rule, input, reviewer, provider result, and time behind each material decision.
The operations layer is equally important. Authorized teams need queues for pending or failed transactions, verification cases, reconciliation differences, disputes, limits, suspicious behavior, customer support, and provider incidents. A safe backoffice offers scoped search and actions, reason codes, approval workflows, export controls, masking, audit history, and links from a customer-visible outcome to the underlying evidence. Direct production-database access is not an operations strategy.
Reporting must distinguish product analytics from financial and regulatory records. Metrics can aggregate and evolve; statements, ledger postings, settlement files, and formal reports need stable definitions, versioned transformations, lineage, and reproducibility. Build export and correction workflows around ownership, deadlines, review, and retention instead of treating reporting as a final dashboard project.
Provider selection deserves the same rigor as software architecture because it shapes the product customers actually receive. Compare supported markets, currencies, payment methods, settlement calendars, reserve rules, fee components, refund and dispute behavior, verification coverage, data location, service objectives, support escalation, reporting detail, sandbox fidelity, and contractual exit terms. Run realistic acceptance journeys before committing: partial captures, duplicate requests, delayed webhooks, disputed payments, expired documents, unavailable banks, rounding at currency boundaries, and reconciliation against real report formats. A low headline transaction fee can be overwhelmed by manual exception work, poor authorization rates, slow settlement, or missing evidence.
A provider abstraction should protect the domain from vendor-specific payloads without pretending every provider is interchangeable. Normalize durable business concepts and error categories, preserve the original messages for evidence, and isolate credentials, signing, retries, rate limits, and version changes inside adapters. Switching providers still requires commercial onboarding, data migration, operational training, and parallel verification. The architectural goal is to make those costs visible and bounded, not to promise a zero-effort swap.
Reliable Financial Architecture and Transaction Control
Financial architecture needs one authority for each fact. The internal platform should not blindly mirror a provider’s status, nor invent certainty when an external outcome is unknown. Model transaction states and legal transitions explicitly. A timeout after submission means “outcome unknown”; it requires status inquiry or reconciliation before a retry, refund, or compensation can safely move value again.
Every money-moving command needs idempotency at the business boundary. Bind a key to the actor, operation, and request fingerprint; persist the original outcome; return it on a legitimate retry; and reject reuse with different inputs. Webhooks require source authentication, replay protection where available, duplicate and out-of-order tolerance, conditional state transitions, durable storage, and controlled retry. A provider’s delivery guarantee does not remove consumer idempotency.
A ledger records immutable postings instead of replacing a balance. Balanced entries, explicit accounts, currencies, precision, value dates, references, and correction postings make deposits, transfers, fees, exchanges, holds, releases, refunds, reversals, and manual adjustments explainable. Available, pending, and accounting balances should have defined derivations. The product may use a provider ledger, an internal ledger, or both, but ownership and reconciliation cannot remain implicit.
Reconciliation is the feedback loop between internal state and external financial reality. Compare transaction, balance, fee, settlement, and payout records at a defined cadence; classify differences; assign an owner and aging target; preserve evidence; and control repair. Monitor mismatch count and value, unknown outcomes, queue age, settlement lateness, and manual adjustments. An alert is useful only when an operator can reach the affected record and follow a tested response.
Keep business capabilities modular before distributing them. Accounts, payments, ledger, compliance cases, limits, notifications, reporting, and provider adapters need clear contracts and ownership. Durable queues help isolate background work, but introduce at-least-once delivery, ordering, backlog, and dead-letter responsibilities. Scale stateless processing only after database connections, provider quotas, serialization points, and reconciliation capacity are understood.
Security, Compliance Evidence, and Operational Transparency
Security starts with an inventory of value, sensitive data, actors, and trust boundaries. Minimize cardholder, personal, identity, and financial data before protecting it. Tokenization and provider-hosted components can reduce exposure, but a documented data-flow review must confirm what enters browsers, logs, queues, analytics, backups, support tools, and third parties. Encrypt data in transit and at rest, separate key management, rotate credentials, and keep secrets out of code, images, URLs, and telemetry.
Authentication establishes identity; authorization decides whether that identity may view or change this account, transaction, document, beneficiary, case, limit, or report. Enforce object and action policy on the server. Privileged operations may need stronger authentication, time-bounded access, separation of duties, dual approval, transaction limits, and reason codes. Test object-ID substitution, mass assignment, replay, enumeration, excessive data exposure, forged webhooks, account recovery, and support impersonation.
Audit evidence must be useful and protected. Record who or what acted, the business object, permitted transition, reason, relevant before-and-after facts, source request or provider event, time, and correlation—not raw credentials or unnecessary personal data. Limit audit access, detect tampering, define retention, and make high-risk sequences reviewable. Logging everything without lineage, search, and ownership creates cost rather than control.
Compliance scope follows the product, markets, licensed entities, processors, data, and contractual roles. Qualified legal, compliance, security, and regulated partners determine obligations such as licensing, AML, sanctions, consumer protection, privacy, reporting, PCI DSS, and operational resilience. Engineering maps those obligations to controls, evidence, supplier records, tests, incident handling, recovery, and change management; it does not award certification or replace accountable policy owners.
Operational resilience covers bad releases, unavailable providers, delayed settlement, database failure, credential compromise, fraud spikes, zone or region loss, and human error. Define RTO and RPO by capability, backups and restore tests, degraded modes, provider failover rules, incident authority, regulatory or customer communication, and reconciliation after recovery. A managed cloud service reduces infrastructure work but does not prove that the financial process survives failure.
A reliable FinTech platform makes every financial movement explainable: what changed, why it changed, who or what initiated it, which record is authoritative, and how the result was confirmed.
— GARNO.TECH
Build the Smallest Responsible FinTech Product
The right first release is the smallest end-to-end financial capability that can be operated responsibly. It may serve one market and customer segment through one funding and payout path, with explicit limits and manual review. It still needs truthful states, transaction integrity, reconciliation, permissions, support tooling, monitoring, incident response, backups, recovery, and a way to explain every exception.
Start discovery with decisions rather than a feature inventory. Clarify the value flow, licensed and contractual roles, provider shortlist, data boundary, ledger ownership, transaction volumes, service objectives, reporting obligations, operational team, and launch evidence. Resolve the uncertainties capable of changing architecture or cost through documentation, provider validation, prototypes, or production-shaped tests.
Define launch measures before development turns activity into momentum. Track completion and abandonment by journey, authorization and verification outcomes by explainable category, time to final state, settlement punctuality, reconciliation breaks, manual touches per transaction, support contacts, fraud and loss signals, provider availability, and unit economics after exception handling. Set thresholds and owners for release, expansion, degradation, and rollback. A growing payment count is encouraging, but it does not reveal whether balances agree, customers understand delays, or operations can sustain the workload.
Before launch, rehearse a full operating day with support, finance, risk, compliance, and engineering: assign incoming cases, approve a sensitive action, investigate a mismatch, communicate a delay, restore a failed job, and close the evidence trail. This exposes missing permissions, instructions, ownership, and escalation paths while the stakes remain controlled.
Delivery should promote immutable, traceable artifacts through controlled environments. Infrastructure as code, federated CI/CD identity, secret isolation, dependency and image scanning, compatible database migrations, progressive exposure, and tested rollback reduce change risk. Quality assurance covers state transitions, permissions, idempotency, concurrency, duplicate and reordered events, provider timeouts, limits, reconciliation, migration, restore, and operator recovery—not only the happy customer path.
Modernization follows the same discipline. Map financial truth and operational workarounds, place a stable contract around the capability being changed, compare old and new records, run in shadow or parallel where justified, move traffic gradually, and define exit criteria before migration. A big-bang rewrite is warranted only when evidence shows incremental paths are less safe or economical.
Financial migration needs control totals at every boundary. Inventory open transactions, balances, holds, beneficiaries, mandates, limits, identity cases, disputes, and historical statements; define which system owns each item during transition; and preserve old identifiers for traceability. Rehearse transforms with production-shaped data, reconcile counts and values by currency and state, sample individual histories, quarantine ambiguous records, and require named approval for differences. After cutover, monitor both expected business activity and silent failure signals such as missing files, empty queues, unchanged balances, or an implausible absence of exceptions.
Share the users, markets, providers, money flows, current constraints, and outcome you need. We can shape a new platform, a focused MVP, a provider replacement, a ledger or reconciliation capability, an operations backoffice, or a staged modernization plan with explicit assumptions, ownership, and acceptance evidence.
Publications
Our research
Research and development of AI-powered solutions to optimize business workflows and enhance decision-making processes.
Analysis of machine learning models for predictive analytics in finance, e-commerce, and SaaS platforms.
Exploration of natural language processing and computer vision technologies to strengthen automation, personalization, and customer support.
Enterprise Software Solutions for Controlled, Adaptable Operations
Design enterprise software around capabilities, workflows, systems of record, integrations, identity, controls, data governance, reliable delivery, operations, and incremental legacy modernization.
9 min read
24 Jul 2026
How to Choose a FinTech Development Company: 10 Evidence-Based Criteria
Evaluate FinTech development companies through product evidence, financial workflows, security, compliance, integrations, architecture, testing, delivery, contracts, and support.
12 min read
30 Jul 2026
How to Estimate FinTech App Development Cost Without False Precision
Turn FinTech scope, transaction risk, regulatory evidence, provider dependencies, team capacity, and operations into a budget range that can be governed and revised.
9 min read
05 Aug 2026