Angular SSR and Hydration: Design the Whole Request Lifecycle
- Angular SSR
- Angular hydration
- server-side rendering
- Core Web Vitals
- Angular Universal
How to Design Angular SSR and Hydration for Production
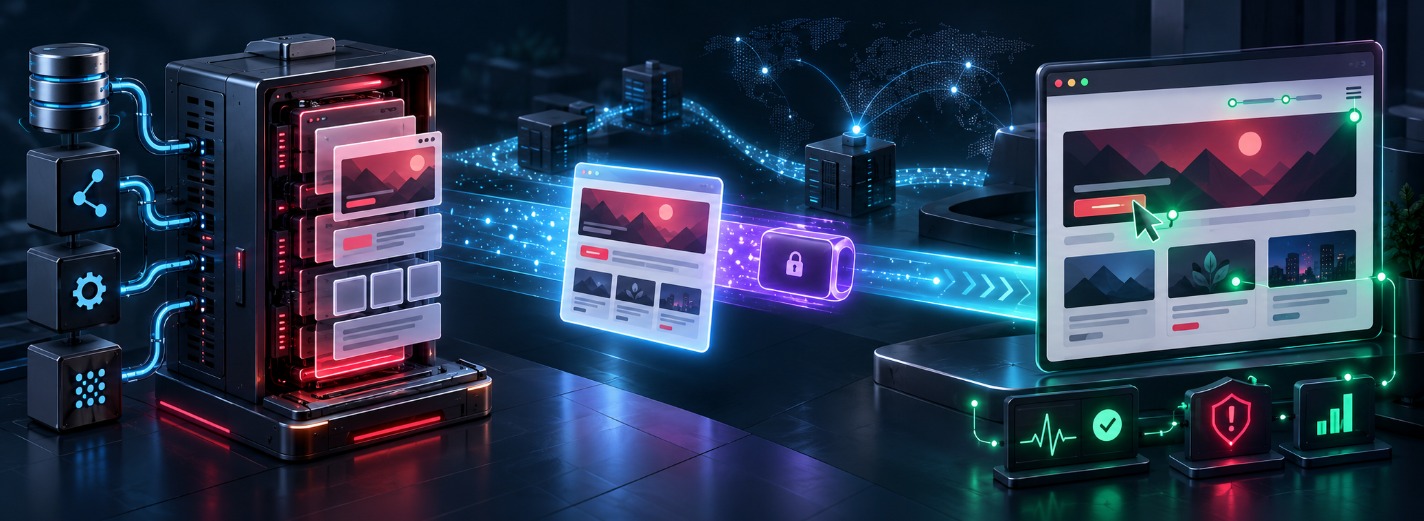
Server-side rendering is an operating model, not an SEO switch. It adds an execution environment that runs application code per request, obtains data, makes identity and cache decisions, produces HTML, serializes selected state, and then hands the page to a browser that must hydrate the same component tree. Every step creates latency, security, capacity, correctness, deployment, and incident behavior that a client-only application does not have.
Begin with user outcomes by route: discoverability, time to useful content, interaction readiness, freshness, personalization, privacy, offline behavior, device capability, traffic shape, and business criticality. Record the current field metrics and crawler or conversion evidence. Angular supports a hybrid model in which routes can use client rendering, build-time prerendering, or request-time server rendering. Use that flexibility to solve measured problems rather than serving every page through the most complex path.
Choose CSR, Prerender, or SSR Route by Route
Classify every route. CSR fits highly interactive authenticated workspaces, offline-capable experiences, or routes whose content is not useful until authorization and live data arrive. Prerendering fits stable public content with enumerable paths and a build-time freshness model. SSR fits request-specific or frequently changing content that benefits from complete initial HTML. A hybrid product can apply all three without treating one as the default for unrelated journeys.
For each route, document data sources, identity, personalization, cacheability, revalidation, expected traffic, server cost, failure fallback, navigation after hydration, metadata, localization, and acceptance metrics. Prerendering moves work to build time and can multiply output by locale and parameter. SSR moves work to request time and couples availability to the render server and its dependencies. CSR shifts more work and data fetching to the browser.
Prove representative routes before broad adoption: one public static route, one dynamic public route, one authenticated journey, and one route with a browser-heavy library. Compare field LCP and interaction latency, HTML completeness, JavaScript weight, server latency, cache behavior, crawl output, errors, accessibility, and cost. A route should retain SSR only when the measured benefit exceeds the additional operating surface.
Enforce Browser and Server Boundaries
Server execution has no browser DOM, layout, storage, history, media query, observer, canvas, or many third-party globals. Audit direct and transitive use of window, document, local or session storage, layout measurement, timers, randomness, geolocation, and DOM-mutating libraries. Put environment behavior behind injected abstractions or platform-specific providers so business components do not scatter runtime checks.
Defer browser-only initialization until the browser render lifecycle. Prefer server-compatible libraries or isolated client-only islands for editors, maps, charts, media players, analytics, advertising, and widgets. Third-party scripts that modify the DOM before hydration can create mismatches; load them after hydration where possible. Use skip-hydration only as a bounded exception with an owner, performance impact, and replacement plan.
Treat the render server as a multi-request service. Request identity, locale, authorization, feature decisions, and mutable state must not leak through module-level singletons or top-level provider values reused across requests. Bound outbound hosts and validate user-influenced URLs to reduce SSRF risk. Keep secrets on the server, but never serialize them into HTML, transfer state, logs, or error pages.
Keep Server and Client Output Deterministic
Hydration reuses server-rendered DOM by matching it to the client application. The initial structures must agree. Inject a request-stable clock, locale, time zone, randomness, feature decisions, and initial data rather than reading changing defaults independently. Avoid rendering different branches with browser checks in templates. Sort data explicitly and give repeated items stable domain identity.
Validate generated HTML. Invalid nesting, implicit browser correction, direct DOM mutation, whitespace assumptions, and third-party scripts can make the browser tree differ from server output. Test development diagnostics and production builds because timing and optimization differ. Capture hydration errors with route, release, component boundary, locale, browser, and sanitized request context so the team can reproduce the mismatch.
Design the interval between visible HTML and attached interaction. Angular event replay can capture supported events before hydration and replay them afterward; incremental hydration can delay selected boundaries until triggers such as interaction or visibility. Test rapid clicks, focus, form entry, navigation, nested deferred regions, slow JavaScript, assistive technology, and failure. Prevent duplicate submissions and make actions idempotent rather than assuming event replay removes every race.
Design Authentication Before Shared Caching
Classify responses as public, safely segmented, personalized, or forbidden to cache before writing cache rules. Specify which cookies or tokens the render server receives, how sessions are validated, whether credentials are forwarded to APIs, and what authorization occurs at each data boundary. HTML visibility is not authorization; APIs must enforce access independently.
For every cache layer—browser, CDN, reverse proxy, render cache, application cache, and transfer cache—define key dimensions, TTL, revalidation, invalidation, stale policy, purge, and sensitive-data exclusions. Include host, path, query, locale, currency, experiment, device class, and identity segment only when they truly change output. A missing key dimension can expose one user or tenant to another.
Test authenticated and anonymous requests in alternating order, multiple tenants, login and logout, role change, session expiry, cache warm and cold states, and failure during revalidation. Inspect actual CDN and proxy headers and stored objects. Prefer no shared caching for personalized HTML unless isolation has been proven. Performance gains never justify ambiguous privacy boundaries.
Control Transfer State and Serialized Data
Transfer state can prevent the browser from immediately repeating eligible data requests made during server rendering. Define exactly which requests and fields may be serialized. Angular provides HTTP transfer-cache controls and excludes many credentialed or explicitly private responses by default, but custom filtering can weaken those protections. Treat the generated HTML as data visible to the browser, intermediaries, monitoring, and anyone allowed to view source.
Transfer the smallest representation needed for the initial route. Exclude secrets, tokens, internal identifiers, excessive records, unrelated permissions, and fields hidden only by CSS. Version serialized shapes and validate them at the boundary. When server and browser use different API origins, map them deliberately rather than disabling identity checks. Measure HTML growth, parse cost, duplicate requests, and freshness.
Choose failure behavior for missing or stale transferred data. The client may refetch, show a bounded stale view, retain server HTML until fresh data arrives, or move to an explicit error state. Prevent a late browser response from overwriting newer interaction. Test navigation away and back, slow hydration, cache bypass, mutation during hydration, session change, and partial API failure.
Set Timeout, Capacity, and Degradation Rules
Give the whole SSR request a deadline and allocate budgets to authentication, cache lookup, each API, rendering, serialization, and response streaming. Propagate cancellation where possible. Apply bounded retries only to transient and idempotent work; repeated calls inside a render can amplify an outage. Limit concurrency, connections, payload, and per-request memory before saturation turns one slow dependency into a render-server collapse.
Define useful degradation by route: cached public HTML, a client-rendered shell, partial content, delayed noncritical region, maintenance response, or controlled error. Preserve correct status codes, metadata, canonical links, privacy, and retry behavior. A fallback that returns HTTP 200 with an empty or incorrect page can mislead users, monitors, and crawlers more than an explicit failure.
Capacity-plan cold start, steady traffic, crawlers, bursts, bots, cache miss, dependency latency, memory, garbage collection, and deployment overlap. Autoscaling reacts after demand and may not protect a sudden miss storm. Use admission controls, bot and rate policy, CDN protection, headroom, readiness, graceful draining, and rollback. Load-test full routes with realistic data and downstream timing, then rehearse cache and provider failures.
Observe the Complete Server-to-Hydration Request
Trace a page from CDN or edge through render server, authentication, cache, APIs, template rendering, serialization, response, resource loading, hydration, event replay, and interactive work. Propagate correlation context without exposing sensitive data. Attach route mode, cache status, release, locale, identity class, response status, fallback, hydration outcome, and browser navigation to structured telemetry.
Measure server response distribution, render duration, dependency time, cache hit and age, errors, timeouts, aborts, memory, CPU, concurrency, cold starts, HTML and transfer-state bytes, client resource and JavaScript weight, field content and interaction metrics, layout shift, hydration duration, mismatches, replayed events, and route conversion or task completion. Average latency hides the expensive tail that consumes capacity.
Build dashboards and alerts around user impact and saturation, then link them to runbooks. Distinguish render failure, dependency failure, cache error, crawler spike, client hydration issue, and application error. Retain enough server and browser evidence to connect the two halves without logging tokens or personal content. Measure cost per rendered response and incremental business benefit so SSR remains an accountable choice.
Roll Out by Route with Evidence and Rollback
Pilot a small set of representative routes behind controlled exposure. Establish baseline field metrics, crawl output, conversion or completion, errors, server capacity, cache behavior, and hosting cost. Validate HTML snapshots semantically, route metadata, status and redirects, privacy isolation, accessibility, hydration, interaction before hydration, client navigation, and rollback.
Release by route or traffic cohort with a stop rule. Keep the previous CSR or prerender path available where feasible, and avoid coupling SSR rollout to unrelated redesign or backend change. Compare field rather than laboratory metrics across devices, networks, browsers, users, and crawlers. Watch tail latency and dependency load as caches warm and traffic shifts.
Expand only when production evidence supports the route model and the team can operate it. Review mode assignments when content, privacy, traffic, personalization, infrastructure, or product goals change. Document server and browser boundaries, cache and transfer rules, deadlines, fallback, capacity, dashboards, incident roles, deployment, and rollback. Successful SSR is a maintained delivery system, not a one-time rendering milestone.
- Classify every route: choose CSR, prerender, or SSR from discoverability, freshness, personalization, privacy, interaction, traffic, failure, cost, and field evidence.
- Enforce execution boundaries: isolate browser APIs and DOM-mutating libraries, keep request state out of shared singletons, bound outbound hosts, and preserve deterministic markup.
- Protect private data: define credential forwarding, authorization, cache classes and keys, transfer-state allowlists, serialization limits, expiry, and purge before optimization.
- Bound the request: allocate dependency deadlines, cancellation, retry and concurrency limits, memory budgets, useful fallbacks, admission control, capacity headroom, and graceful draining.
- Observe both halves: connect edge, render server, APIs, cache, HTML, transfer state, hydration, event replay, interaction, errors, user outcomes, and cost by route and release.
- Roll out with evidence: pilot representative routes, test privacy and failure, compare field metrics, expose traffic gradually, enforce a stop rule, and retain a verified rollback path.
What should we decide first for Angular SSR and hydration?
What should we decide first for Angular SSR and hydration?
How should Angular SSR and hydration be tested?
How should Angular SSR and hydration be tested?
What is the largest implementation risk?
What is the largest implementation risk?
Does every Angular product need the same rendering approach?
Does every Angular product need the same rendering approach?
When should we ask for an external review?
When should we ask for an external review?
Plan Angular SSR Around Real Routes
Share the route map, user and crawler goals, identity and data flows, current field metrics, browser-only dependencies, hosting and CDN, cache rules, traffic, availability, incident evidence, and release constraints. GARNO.TECH can design and prove a hybrid rendering model with safe hydration, privacy boundaries, transfer controls, capacity, observability, staged rollout, rollback, and knowledge transfer.
Publications
Our research
Research and development of AI-powered solutions to optimize business workflows and enhance decision-making processes.
Analysis of machine learning models for predictive analytics in finance, e-commerce, and SaaS platforms.
Exploration of natural language processing and computer vision technologies to strengthen automation, personalization, and customer support.
Angular Performance Optimization for Data-Heavy Applications
Optimize data-heavy Angular applications through representative profiling, bounded DOM and computation, deliberate state updates, virtualization, chart control, route budgets, leak prevention, and field evidence.
9 min read
08 Sep 2026
Angular Authentication Security: Design the Trust Boundary First
A production guide to Angular authentication architecture: browser and BFF sessions, OIDC with PKCE, cookie and token threats, refresh, XSS, CSRF, CORS, logout, revocation, authorization UX, and safe observability.
11 min read
08 Sep 2026
Angular Deployment on Azure: Architecture, Security, and Release Guide
A practical guide to deploying Angular on Azure: choose the right runtime, configure SPA routing and runtime settings, design caching and edge security, build a reversible pipeline, and observe the complete user path.
12 min read
08 Sep 2026