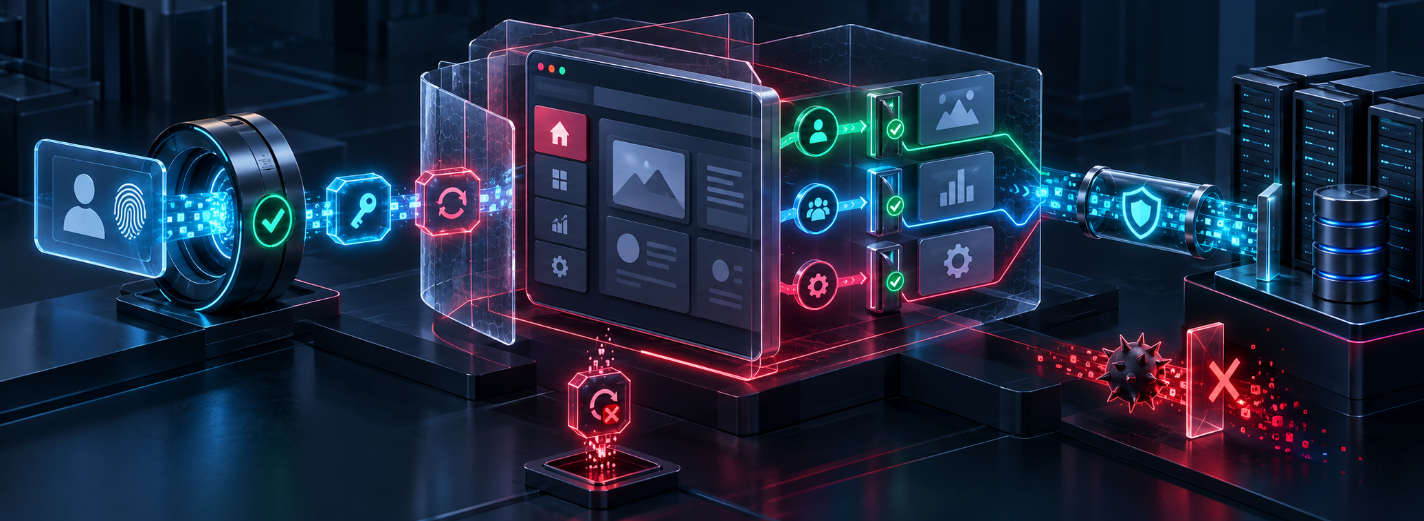
Angular Authentication Security: Design the Trust Boundary First
- Angular security
- Angular authentication
- OIDC
- session security
- frontend authorization
How to Design Secure Authentication Architecture in Angular
Angular can render an authentication interface, guard navigation, attach request context, and maintain a useful local session view. It cannot make the browser a trusted authorization authority. Code, storage, route guards, hidden controls, and network calls on the user’s device can all be inspected or changed. APIs and a trusted backend must validate identity, audience, permissions, resource ownership, workflow state, and every security-sensitive command.
Begin with assets and attack paths rather than an authentication library. Map the browser, hosting origin, backend for frontend, APIs, identity provider, third parties, administrator channels, cookies, tokens, personal data, and audit evidence. Include XSS, CSRF, token theft, login CSRF, redirect abuse, session fixation, account enumeration, compromised dependencies, malicious extensions, shared devices, concurrent tabs, replay, and insider access. Then choose a session architecture whose residual risks the organization can operate and explain.
Define Assets, Actors, and Trust Boundaries
Draw each trust boundary and data flow: authorization redirect, callback, code exchange, session creation, API call, refresh, step-up authentication, logout, revocation, and audit. For every edge, record the caller, credential, expected issuer and audience, transport, origin, replay defense, timeout, error behavior, and log policy. A sequence diagram often exposes assumptions that disappear inside an SDK configuration.
Separate authentication, session management, and authorization. Authentication establishes who controls an identity at a point in time. A session carries that result with bounded lifetime and assurance. Authorization decides whether the actor may perform this action on this resource now. Angular may use capabilities to present the right interface, but the server must enforce policy with current data. A decoded token is input to verification, not proof by itself.
Define security objectives and recovery: acceptable session lifetime, idle timeout, step-up conditions, device and tenant switching, compromised-account response, revocation delay, availability, privacy, audit retention, and support workflow. Identify who owns the identity provider, BFF, API policy, frontend integration, security headers, secrets, monitoring, and incident decisions. Threat-model representative journeys and retest boundaries when origins, providers, embedded content, mobile clients, or regulatory obligations change.
Choose a Session Pattern from the Threat Model
A same-origin BFF can keep OAuth access and refresh tokens out of JavaScript and expose an opaque session cookie to the browser. Configure the cookie with Secure, HttpOnly, an appropriate SameSite policy, narrow Path and host scope, rotation, and server-side expiry. The BFF adds infrastructure, state, CSRF responsibility, proxy authorization, capacity, and outage behavior, but can materially reduce token-exfiltration paths.
A browser-only public client may obtain tokens through Authorization Code with PKCE when its deployment and identity provider support the required controls. It cannot keep a client secret. Prefer short-lived access tokens held in memory, narrowly scoped audiences, sender constraints where available, refresh-token rotation under provider guidance, and deliberate recovery after reload. Persistent browser storage increases exposure to injected code, extensions, shared machines, backups, and stale sessions; choose it only from an explicit threat and usability analysis.
Cookies and bearer tokens fail differently, and neither makes XSS harmless. An HttpOnly cookie may resist direct reading, yet injected code can still issue authenticated actions from the page; a readable token may also be exfiltrated and replayed elsewhere. Document which threats each control reduces, which remain, and how quickly detection and revocation work. Avoid custom cryptography, home-grown token formats, credentials in URLs, and a single interceptor that silently defines the entire security model.
Use Standards-Based OIDC Flows and Validate Every Boundary
Use OpenID Connect for authentication and OAuth for delegated API access. For browser-based clients, use Authorization Code with PKCE rather than implicit flow. Generate high-entropy state, nonce, and PKCE verifier values for the transaction, bind them to the initiating browser context, enforce exact registered redirect URIs, and remove authorization artifacts from visible URLs and history as soon as the protocol permits.
Use a maintained, standards-conformant library and pin trusted issuer configuration. Validate issuer, audience, signature, algorithm policy, expiry, not-before time, nonce, authorization response, and token type in the component responsible for verification. The API must accept only tokens minted for that API and authorize scopes or claims against server-side resource policy. Do not use an ID token as a general API access token or trust roles merely because the UI decoded them.
Design abnormal flows: user cancels, callback opens in another tab, state is missing, the authorization server is unavailable, consent or MFA is required, clocks differ, keys rotate, a tenant is wrong, or a redirect resumes after deployment. Use a dedicated callback route with minimal dependencies and safe error text. Test mix-up, code replay, open redirect, login CSRF, account linking, prompt behavior, deep-link restoration, and provider logout against the provider’s conformance profile.
Coordinate Expiry, Renewal, and Concurrent Requests
Model session time explicitly: access-token expiry, server-session absolute and idle limits, refresh eligibility, clock skew, last verification, and required assurance. Renew early enough to finish important work but add jitter so a deployment or shared expiry does not produce a refresh storm. A client timer is a user-experience hint; the server remains authoritative and may revoke or reject a session at any request.
Coordinate renewal through one owner. When many requests encounter expiry, start one refresh and queue, retry, or fail dependents according to idempotency and user intent. Never create an interceptor loop in which refresh requests trigger themselves. Bound retries, preserve cancellation, and distinguish network failure, expired session, revoked credential, consent requirement, and provider outage. Across tabs, coordinate carefully without broadcasting credentials; a server session check or minimal cross-tab signal is safer than sharing tokens.
Preserve unsaved work without weakening session policy. On expiry, suspend sensitive actions, retain allowed local drafts, reauthenticate, re-fetch capabilities and server versions, then reconcile before submission. Step-up authentication should bind to the intended high-risk action and expire quickly. Test expiry during upload, payment, streaming, offline work, route preloading, SSR, background tab throttling, device sleep, simultaneous tabs, key rotation, revoked refresh token, and timeout after a server commit.
Treat XSS as a Session-Level Incident
Any arbitrary script running in the application origin can act with the user’s privileges. Angular treats template-bound values as untrusted and sanitizes them by security context, but direct DOM APIs, third-party widgets, dynamic script loading, unsafe HTML, and bypassSecurityTrust* can cross that boundary. Never build Angular templates from user data. Keep AOT enabled, audit every trust bypass, and construct trusted values as close as possible to a small validated source.
Deploy defense in depth with a restrictive Content Security Policy and Trusted Types enforcement where supported. Inventory scripts, styles, frames, connections, workers, forms, and navigation before writing the policy; avoid broad wildcards and permanent report-only mode. Generate nonces correctly per response or use a hosting-compatible hash strategy, and test CDN caching. Pin, review, and minimize dependencies; protect the build and release path; remove unused scripts; and isolate third-party content in constrained frames or origins.
Reduce the value of an XSS foothold: keep long-lived credentials out of JavaScript where feasible, shorten session lifetime for sensitive products, require server authorization and step-up for dangerous actions, use idempotency and transaction confirmation, and redact data already present in the page. Monitor CSP and Trusted Types violations without treating reports as perfect detection. Test stored, reflected, and DOM injection, rich text, URLs, SVG, Markdown, file previews, localization, analytics, support widgets, SSR output, and error pages.
Design CSRF, CORS, and Origin Controls Together
CSRF matters whenever the browser automatically attaches authentication, especially cookies. Use defense in depth: an appropriate SameSite cookie policy, an anti-CSRF token bound to the session, server validation of trusted Origin or Referer where suitable, and custom request headers for API mutations. Angular’s XSRF support helps implement a cookie-to-header pattern, but the server must issue and verify the token and the deployment origins must match the configuration.
CORS controls which browser origins may read or send certain cross-origin requests; it is not authentication or API authorization. Allow exact origins, methods, and headers; never combine credentialed access with a reflected arbitrary origin. Include preflight, redirects, errors, CDN behavior, caches and Vary: Origin in tests. Validate WebSocket origin and authentication separately. Keep state-changing operations away from GET and reject simple cross-origin submissions where the API contract expects JSON and CSRF headers.
Map the real site topology before choosing SameSite: application and API hosts, identity-provider redirects, embedded contexts, custom domains, legacy subdomains, and federated logout. Domain-wide cookies let every subdomain influence a shared credential boundary, so prefer host-only scope and separate untrusted applications. Test malicious origins, sibling subdomains, missing and mismatched CSRF tokens, null origin, preflight cache, redirects, login CSRF, cross-site form posts, and APIs called outside the browser.
Make Logout and Revocation End the Right Sessions
Define what “log out” means: end only this application session, all sessions for this account, the identity-provider session, selected devices, delegated tokens, offline grants, or administrator impersonation. Clear the server session first, expire cookies with matching attributes, revoke eligible credentials, and then clear in-memory identity, private caches, queued requests, drafts according to retention policy, service-worker data, and cross-tab state. A redirect to the login screen alone is not logout.
Use supported OpenID Connect logout mechanisms when federated session termination is required, and validate post-logout redirects and state. Front-channel, back-channel, and RP-initiated logout have different delivery and availability properties; do not promise instant global logout if the ecosystem cannot provide it. Rotate or invalidate sessions after password reset, account recovery, role or tenant change, suspected theft, administrator action, and changes in required assurance.
Design revocation for both security and availability. Cache policy or token decisions only within a defined staleness window, protect introspection and session stores from overload, and decide fail-open or fail-closed behavior per action risk. Provide users with active-session visibility and device revocation where appropriate. Test logout offline, provider outage, concurrent tabs, back-button cache, refresh racing with revocation, long API requests, WebSockets, stolen session reuse, session-store failover, and rollback during a key or cookie migration.
Observe Abuse and Failure Without Recording Secrets
Define a security event vocabulary across browser, edge, BFF, API, and identity provider: login start and result, callback failure class, session creation and rotation, refresh result, authorization denial, step-up, CSRF rejection, suspicious origin, logout, revocation, account recovery, and administrative change. Carry a correlation ID and safe session or actor pseudonym so responders can reconstruct a journey without recording credentials or personal form content.
Never log authorization codes, access or refresh tokens, session cookies, client secrets, passwords, MFA values, raw identity assertions, full URLs with sensitive query data, or private API bodies. Redact at collection, not only at display, and control access, retention, export, and deletion. Alert on meaningful patterns such as repeated state or nonce mismatch, refresh-token reuse, impossible session rotation, cross-tenant denial spikes, CSRF failure, unusual recovery, or a new CSP violation after release, while rate-limiting attacker-controlled telemetry.
Measure login completion, callback failure, session and refresh latency, renewal storms, authorization denials by reason, forced reauthentication, revocation delay, logout completion, CSRF and CSP signals, provider availability, support cases, and time to contain an incident. Rehearse token or cookie theft, signing-key rotation, provider outage, compromised dependency, accidental secret logging, tenant-isolation failure, and emergency session invalidation. Release authentication changes gradually with compatible cookies and callbacks, explicit stop rules, and a verified rollback that does not restore revoked trust.
- Map trust before code: document assets, actors, origins, redirects, credentials, issuers, audiences, replay defenses, authorization, recovery, owners, and residual risk.
- Choose the session pattern deliberately: compare a same-origin BFF and browser token client by XSS, CSRF, replay, storage, infrastructure, availability, usability, revocation, and operational capability.
- Implement the protocol, not a look-alike: use OIDC Authorization Code with PKCE, strict redirect and transaction binding, maintained libraries, issuer and audience validation, and server-side authorization.
- Contain browser compromise: preserve Angular sanitization, audit trust bypasses, enforce CSP and Trusted Types, reduce third parties, protect dependencies and builds, and limit session value.
- Finish the session lifecycle: coordinate renewal, concurrent requests, expiry, step-up, CSRF and origin controls, logout scope, revocation, cached data, tabs, devices, and federated sessions.
- Operate with safe evidence: correlate security events without secrets, detect abuse, measure user impact and revocation delay, rehearse incidents, stage releases, and verify rollback.
What should we decide first for Angular authentication?
What should we decide first for Angular authentication?
Are secure cookies always safer than tokens in browser storage?
Are secure cookies always safer than tokens in browser storage?
What is the largest implementation risk?
What is the largest implementation risk?
How should an Angular application handle token or session expiry?
How should an Angular application handle token or session expiry?
When should we ask for an external security review?
When should we ask for an external security review?
Make the Authentication Boundary Reviewable
Share the origin and API map, identity-provider configuration, login and logout sequences, cookie or token handling, authorization model, security headers, third parties, session and refresh rules, incidents, telemetry, regulatory needs, traffic, and release constraints. GARNO.TECH can threat-model the architecture, verify protocol and browser controls, test failure and revocation, and deliver prioritized changes with evidence, staged rollout, rollback, runbooks, and knowledge transfer.
Publications
Our research
Research and development of AI-powered solutions to optimize business workflows and enhance decision-making processes.
Analysis of machine learning models for predictive analytics in finance, e-commerce, and SaaS platforms.
Exploration of natural language processing and computer vision technologies to strengthen automation, personalization, and customer support.
Angular SSR and Hydration: Design the Whole Request Lifecycle
A production guide to Angular hybrid rendering, route-level CSR, prerender and SSR, hydration, browser boundaries, deterministic output, authentication, caching, transfer state, degradation, observability, and rollout.
9 min read
08 Sep 2026
Angular with NestJS: Production Full-Stack Architecture
Design Angular and NestJS around clear authority, generated API contracts, secure authentication, recoverable errors, state consistency, SSR boundaries, end-to-end observability and compatible releases.
9 min read
08 Sep 2026
CTO Responsibilities for Security and Cloud Infrastructure: An Accountable Operating Model
Define the CTO mandate for cyber and cloud risk across risk appetite, evidence, control ownership, shared responsibility, incident authority, cost, review, and escalation.
9 min read
08 Sep 2026