Angular with NestJS: Production Full-Stack Architecture
- Angular
- NestJS
- TypeScript
- API contracts
- authentication
- full-stack architecture
How to Architect Angular with NestJS for Production
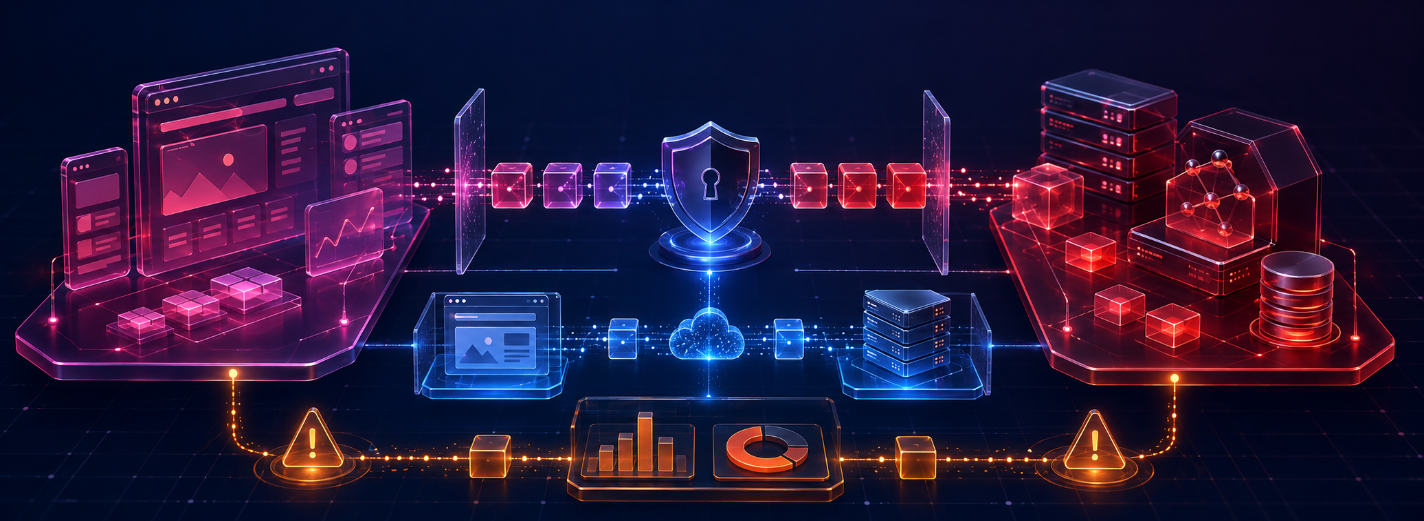
Angular and NestJS work well together because they offer consistent TypeScript tooling on opposite sides of a hard trust boundary. Angular owns browser interaction, accessible presentation and temporary client state. NestJS owns authentication, authorization, business invariants, durable data and integration effects. Sharing a language reduces friction; it does not make browser input trustworthy or permit domain rules to drift into components.
Begin with one critical user journey. Trace it from route and form through the API contract, identity, application rule, database and external dependency, then back through loading, success, empty and failure states. Define latency, availability, security, accessibility, recovery and release requirements. This guide shows how to turn those requirements into boundaries that teams can test and operate.
Separate Browser Experience from Server Authority
Organize Angular by product capability rather than technical folders. A feature boundary can contain its routes, presentation components, orchestration, forms and data access, while shared design primitives remain deliberately small. NestJS can mirror durable business capabilities through modules, controllers, application services, domain rules and adapters. Similar names may aid navigation, but the two codebases do not need identical internal shapes.
The browser may validate for guidance, hide unavailable actions and preserve unfinished input, but NestJS must validate every command and query against the authenticated actor, tenant, resource and current state. Never trust a role, price, owner ID or workflow status supplied by Angular. Keep authorization close to the server operation it protects, and make tenant scope explicit in repository and service interfaces.
A Backend for Frontend can be useful when the browser would otherwise coordinate many services, expose internal topology or repeat policy-heavy aggregation. It should own a client-specific API experience, not duplicate the source systems’ business truth. Introduce it only with a named latency, security or delivery benefit; another network hop and deployment are real operating costs.
Generate Clients from Explicit API Contracts
Choose a contract source that independent consumers can validate. OpenAPI works well for request-response APIs; GraphQL and event schemas have different tooling but the same obligation: describe wire behavior, not internal TypeScript classes. Include required and nullable fields, formats, enums, pagination, error shapes and examples. NestJS decorators may produce a specification, but the published artifact is the boundary.
Generate a narrow Angular client or transport types in CI and fail compatibility checks when a change removes or reinterprets existing behavior. Generation does not replace runtime validation: servers must reject malformed input, and clients must handle responses from mixed versions during rollout. Avoid publishing database entities or domain objects as wire models; their reasons to change are different.
Evolve contracts additively. Add optional fields, support old and new values during a compatibility window, version genuinely incompatible capabilities and publish deprecation dates with observable usage. Consumer-driven tests can protect important assumptions, while end-to-end tests should prove a representative journey. A shared monorepo may speed coordination, but it must not hide a breaking API behind a single green build.
Design Authentication as One Complete Lifecycle
Model authentication as a complete lifecycle: initial navigation, sign-in, callback, session establishment, API access, renewal, permission denial, password or identity changes, revocation and logout. Decide whether a same-site secure cookie, an external identity provider or a token flow fits the hosting topology and threat model. Keep bearer tokens out of browser storage when a safer cookie or server-mediated design is viable.
Angular guards improve navigation but do not authorize data. NestJS must authenticate every protected request and enforce permissions at the resource and action level. Distinguish unauthenticated from authenticated-but-forbidden responses, prevent open redirects, protect cookie-based state changes from CSRF and bound refresh concurrency so several failed requests do not create a token storm.
Test expiry while a form is open, several tabs refreshing together, revoked roles, disabled users, clock skew, identity-provider outage and final logout. Avoid automatic retries for non-idempotent commands. Audit material sign-ins, privilege changes and administrative actions without logging credentials or sensitive claims. Recovery should return the user to a safe, understandable state.
Give Errors Stable Semantics and Recovery
Define an error envelope with a stable business code, safe message, field or object path, correlation identifier and optional retry guidance. HTTP status expresses transport semantics; the business code tells Angular whether an email is already used, an optimistic version is stale or a transition is forbidden. Never expose stack traces, queries, tokens or internal topology to the browser.
Map errors deliberately in Angular. Validation belongs beside the affected control and receives accessible focus and announcement. A conflict should offer refresh, merge or retry according to the workflow. A transient dependency failure may preserve input and permit a bounded retry; a permanent rule failure should explain the next valid action. A global toast is rarely sufficient for recoverable work.
Centralize NestJS exception translation so controllers do not invent incompatible shapes, but retain domain-specific codes. Log the same correlation ID with the technical cause on the server. Test malformed input, authorization, not-found records, conflicts, rate limits, timeouts and unavailable dependencies. Contract tests protect the envelope; end-to-end tests prove that the user can recover.
Coordinate Client State with Server Truth
Separate server state from interface state. NestJS and its data stores remain authoritative for shared resources, permissions and workflow status. Angular may hold route context, drafts, selections and cached query results, but each cache entry needs a stable identity, freshness rule and invalidation event. Avoid copying the same remote object into several stores that can disagree.
Use optimistic updates only when the action is likely to succeed and has a clear correction path. Attach a version or ETag to contested resources, make commands idempotent where retries are possible and let NestJS detect stale writes. After success, merge the authoritative response or invalidate the affected query. After conflict, preserve the user’s work and show what changed.
Model long operations explicitly. Return a job identity, expose status and result, and define cancellation, deduplication and expiry rather than leaving the browser request open. For real-time updates, choose polling, server-sent events or WebSockets from latency and scale needs. Reconnect from a known cursor and reconcile missed events; a live channel is not itself a source of truth.
Set an Explicit and Secure SSR Boundary
Classify routes before enabling server rendering. Public landing, catalogue and editorial pages may need crawlable HTML and fast first content. Authenticated dashboards often gain little because personalized data cannot be shared safely and the application becomes interactive only after hydration. Render each route for a measured user or discovery outcome, not because one mode must fit the entire application.
Use a narrow server-side API client with explicit credentials and timeouts. Never forward the incoming cookie or authorization header to arbitrary destinations. Separate public, tenant and user cache keys; do not cache personalized HTML in a shared layer. Transfer only safe data needed for hydration, escape serialized state and prevent Angular from repeating the same request unnecessarily.
Test direct navigation, crawlers, slow APIs, partial rendering, redirects, locale and tenant selection, hydration mismatch and JavaScript failure. Measure server response, first content, interaction readiness and infrastructure cost separately. Provide loading and error states that work before hydration, and keep browser-only APIs behind explicit boundaries so SSR failures do not appear only in production.
Trace the Journey from Browser to Dependency
Carry a trace or correlation context from the browser action through the edge, NestJS request, database and external calls. Record route or operation names, status, duration, release version and safe tenant context; avoid raw URLs, payloads and user identifiers with unbounded cardinality. Angular errors should include the correlation identifier users can share with support.
Define service indicators around complete journeys: successful login, search, checkout, report generation or another business-critical outcome. Pair availability, latency, errors, saturation and queue age with browser performance and product completion. Instrument deliberate spans around important dependencies, then sample by risk. More telemetry without retention, privacy and cost controls creates noise rather than evidence.
Every alert needs an owner, severity, destination, response expectation and repair guidance. Test it outside office hours and during a dependency failure. Dashboards should answer whether customers are succeeding, which layer is limiting them and what changed with the latest release. Preserve source maps securely and scrub secrets, tokens and sensitive form data before export.
Deploy Angular and NestJS as Compatible Versions
Angular and NestJS should be independently deployable only when their contracts remain compatible during mixed-version periods. Add fields before using them, keep old behavior through a defined window and remove it after usage falls to zero. Database changes follow expand, migrate and contract: deploy a compatible schema, backfill and switch reads or writes before deleting the old representation.
Build immutable artifacts once and promote them through environments. Gate the API with schema and consumer checks, and exercise the critical journey against the candidate versions. Use feature flags for release control without turning them into permanent branches; every flag needs an owner and removal date. Canary or blue-green delivery needs observable stop thresholds and a rehearsed rollback.
Coordinate when one side requires the other, but avoid a fragile simultaneous release as the default. Record a compatibility matrix, release order, migration state and rollback limits. Monitor product and service signals by version. A deployment is complete when customers succeed, data is consistent and operators can explain and reverse the change—not when both pipelines are green.
- Authority: Angular owns interaction and presentation; NestJS validates identity, permission, workflow and persistent truth.
- Contracts: publish the wire schema, generate narrow clients and check compatibility while mixed versions remain deployed.
- Identity: specify sign-in, renewal, denial, revocation and logout end to end; enforce resource authorization on the server.
- Failures: return stable business codes and correlation IDs, then map them to accessible, workflow-specific recovery.
- State: define cache identity, freshness, invalidation, version conflicts, idempotent commands and authoritative reconciliation.
- Operations: classify SSR routes, propagate trace context and release backward-compatible API and database changes with rollback.
What should Angular own and what should NestJS own?
What should Angular own and what should NestJS own?
Should Angular and NestJS share TypeScript types?
Should Angular and NestJS share TypeScript types?
Is a Backend for Frontend required?
Is a Backend for Frontend required?
Does every Angular route need SSR?
Does every Angular route need SSR?
Can Angular and NestJS deploy independently?
Can Angular and NestJS deploy independently?
Make the Angular and NestJS Boundary Reviewable
Share the critical journeys, repositories, API schema, identity flow, deployment topology, service objectives and current incidents. GARNO.TECH will identify the highest-risk boundaries and define a focused architecture or implementation step with acceptance and ownership.
Publications
Our research
Research and development of AI-powered solutions to optimize business workflows and enhance decision-making processes.
Analysis of machine learning models for predictive analytics in finance, e-commerce, and SaaS platforms.
Exploration of natural language processing and computer vision technologies to strengthen automation, personalization, and customer support.
Angular Authentication Security: Design the Trust Boundary First
A production guide to Angular authentication architecture: browser and BFF sessions, OIDC with PKCE, cookie and token threats, refresh, XSS, CSRF, CORS, logout, revocation, authorization UX, and safe observability.
11 min read
08 Sep 2026
Angular SSR and Hydration: Design the Whole Request Lifecycle
A production guide to Angular hybrid rendering, route-level CSR, prerender and SSR, hydration, browser boundaries, deterministic output, authentication, caching, transfer state, degradation, observability, and rollout.
9 min read
08 Sep 2026
Angular Deployment on Azure: Architecture, Security, and Release Guide
A practical guide to deploying Angular on Azure: choose the right runtime, configure SPA routing and runtime settings, design caching and edge security, build a reversible pipeline, and observe the complete user path.
12 min read
08 Sep 2026