Microservices vs Monolith: Choosing the Right Architecture
- microservices vs monolith
- software architecture
- monolithic architecture
- microservices architecture
- system design
- scalable software
- distributed systems
- enterprise software architecture
- modular monolith
- application modernization
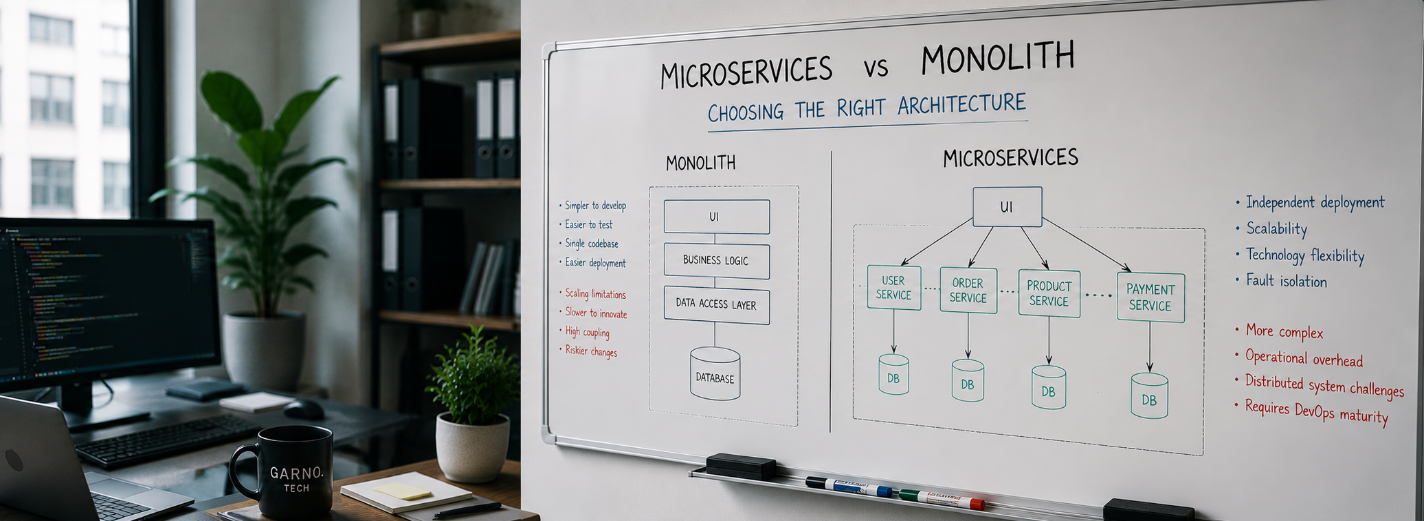
The choice between a monolith and microservices is a choice about where a system pays for coordination. A monolith coordinates most changes inside one codebase, process, deployment, and often one transactional data boundary. Microservices move coordination into explicit service contracts, networks, messages, independent releases, ownership, and operations. Neither removes complexity; each places it where a different organization may handle it better.
Architecture should improve the company’s ability to change a product safely at the required speed. Compare actual constraints: domain stability, number and autonomy of teams, release contention, workload differences, data consistency, availability and recovery objectives, regulatory isolation, platform capability, and total operating cost. Traffic alone rarely decides the model. A well-engineered application can scale far before it needs dozens of services, while organizational coupling can justify separation before raw compute does.
The practical default for many new products is a modular monolith: one deployable system with enforced internal boundaries, explicit ownership, and interfaces that prevent every module from reaching every table. It keeps local development, transactions, testing, and operations simpler while preserving options. Adopt microservices when specific boundaries need independent ownership, deployment, scaling, isolation, or technology badly enough to pay their continuing distributed-system cost.
Treat the decision as a reviewable hypothesis. Record the constraint, expected benefit, operational cost, owner, acceptance evidence, and date for reconsideration. This keeps architecture connected to observable product and organization needs as both evolve.
A Monolith Is a Deployment Choice, Not a Design Failure
A monolithic application is built and released as one principal unit. That says nothing about the quality of its internal design. A modular monolith can organize capabilities into cohesive modules, expose narrow interfaces, own data by domain, prevent cyclic dependencies, and keep business rules independent of delivery frameworks. One artifact may contain many well-governed boundaries.
The operational advantages are substantial: one local runtime, fewer deployment pipelines, direct calls instead of unreliable networks, simpler tracing, atomic transactions where appropriate, fewer version combinations, and a smaller platform surface. Small teams can spend more attention on customer value, domain understanding, and quality. Horizontal replicas, caching, queues, database tuning, read models, and background workers can address many scaling needs without service extraction.
Failure comes from uncontrolled coupling, not the word monolith. Shared tables accessed from anywhere, cross-module imports, global state, long builds, fragile releases, and unclear ownership turn change into negotiation. Measure change failure, test duration, deployment risk, hotspot contention, and module dependencies. Strengthen boundaries before adding a network. Events can decouple work inside or outside one deployment; see Event-Driven Architecture with NestJS. CQRS is also independent of the deployment count; see CQRS with NestJS: Benefits and Trade-Offs.
Microservices Buy Independence with Distributed-System Cost
Microservices divide a system into independently deployable services aligned with business capabilities. A useful service owns meaningful behavior and its data, has a team accountable from design through production, and can evolve without synchronized release of the whole platform. An HTTP endpoint in a separate container that shares a database and release calendar is distribution without independence.
The benefit appears when boundaries carry different needs: several teams must release autonomously; a workload has distinct scaling, security, availability, recovery, or technology requirements; failure must be isolated; or a domain can change on its own schedule. The cost appears in every call and operation: latency, timeouts, retries, duplicate and out-of-order messages, partial failure, eventual consistency, schema evolution, service authentication, discovery, routing, observability, incident coordination, and more infrastructure.
Independent deployment requires compatibility discipline. Services need owned contracts, consumer-aware testing, version and deprecation policies, idempotency, bounded retries, correlation, capacity controls, and recovery playbooks. Each must be deployable and operable without a coordinated ceremony. If every change crosses repositories, waits for a shared test environment, and releases as a train, the result is a distributed monolith with a higher failure surface.
Compare the Trade-Offs That Affect Real Delivery
Delivery: a monolith offers one change path and low setup cost; microservices can reduce coordination only when autonomous teams own stable boundaries. Data: a monolith can use local atomic transactions; services need explicit ownership, events or workflows, reconciliation, and compensation for cross-boundary outcomes. Testing: one process is easier to reproduce; distributed behavior needs contract, integration, resilience, and production-like testing.
Reliability: a monolith has fewer network failure modes but a larger deployment blast radius. Services can isolate failure, yet dependencies can cascade unless timeouts, load shedding, backpressure, and degraded modes are designed and exercised. Scaling: a monolith scales as a unit, though internal workers and read paths can differ; services scale separately, which matters only when the savings or isolation exceed platform overhead.
Security and compliance: one application can centralize controls and reduce the number of identities, secrets, endpoints, and patch targets, but broad internal access increases blast radius. Services can create strong isolation and separate audit boundaries, yet every interface, workload identity, data copy, pipeline, and runtime becomes a control surface. Count the evidence and response work, not only the diagrammed separation.
Cost: count people and cognitive load as well as compute. Every service adds repositories or modules, pipelines, identities, dashboards, alerts, patching, contracts, on-call knowledge, and lifecycle work. Change: compare lead time, deployment frequency, change failure, recovery, and cross-team waits. Ownership: a service without a durable team becomes an orphan; a monolith without enforced module owners becomes a commons. The architecture should make responsibility clearer, not merely move it.
Choose from Constraints, Not Architecture Fashion
Prefer a monolith or modular monolith when the product and domain are still changing, one or a few teams collaborate closely, most capabilities share service objectives, strong consistency is common, and rapid learning matters more than independent release. Establish module boundaries, architecture tests, clear data ownership, observability, automated delivery, and production ownership early. These disciplines create value now and preserve future extraction options.
Consider microservices when evidence shows stable domain boundaries and a recurring need for independence. Look for sustained release contention between autonomous teams, materially different capacity profiles, isolation required by risk or regulation, distinct availability and recovery objectives, or a capability that benefits from a separate lifecycle or technology. Confirm that a team will own each service, including incidents, dependencies, cost, upgrades, and decommissioning.
Test organizational readiness: reliable CI/CD, infrastructure automation, secret and identity management, contract testing, centralized telemetry with distributed traces, service catalogues, incident command, capacity management, security response, and platform support. These are continuing capabilities, not a one-off setup project. Use a weighted decision record with observed constraints, options, consequences, assumptions, and a review trigger. “We may scale someday” is an assumption; measured saturation or persistent team blockage is evidence.
Prefer the option whose mistakes are cheaper to reverse. Internal boundaries can become network boundaries later, while premature services often lock teams into contracts and operational work before they understand the domain. Record what evidence would change the decision: team growth, release waits, measured saturation, isolation requirements, failure history, or rising platform toil. Architecture is a governed hypothesis, not a permanent identity.
Extract Services Only When the Boundary Earns Its Cost
Do not begin migration with a target service count. Begin with a measurable constraint and a candidate boundary. First make the boundary visible inside the monolith: assign ownership, narrow its interface, remove circular dependencies, stop uncontrolled database access, add characterization and contract tests, and measure its change and runtime behavior. Distribution amplifies an unclear boundary; it does not repair one.
Select a candidate with cohesive business responsibility, limited transactional coupling, an identifiable consumer contract, and a concrete benefit such as independent scaling, isolation, release, or ownership. Define success before extraction: reduced lead time or blast radius, lower resource cost, a separate service objective, fewer cross-team waits, or clearer incidents. Avoid central ledger, identity, or highly connected orchestration as a casual first experiment unless that boundary and its consistency model are already well understood.
Use incremental replacement. Route a controlled slice to the new service, establish exclusive data ownership, publish compatible contracts or events, reconcile state, observe both paths, and retain a tested fallback until confidence grows. Design timeouts, idempotency, retries, duplicate handling, ordering, backpressure, authentication, traces, alerts, runbooks, and deployment rollback before traffic depends on them. Never leave permanent direct access to the old database as the hidden integration.
Plan coexistence as a first-class operating state. Decide which system is authoritative for each fact, how writes are routed, how historical data moves, how discrepancies are detected and corrected, and how support staff identify the responsible component. Set a time limit and owner for temporary synchronization paths. Dual writes without a reconciliation model turn rare timing failures into silent data loss.
After each extraction, compare benefit with the new operational load. Stop when the next boundary does not earn its cost. A hybrid architecture is normal: a modular core can coexist with a few independent services and managed providers. The goal is not to complete a migration narrative; it is to remove specific constraints while preserving reliable change.
The best architecture is the smallest set of boundaries that lets real teams change, scale, isolate, understand, and recover the product at the required speed and risk. Every additional boundary must earn its permanent coordination and operating cost over its lifetime.— GARNO.TECH
Design the Smallest Architecture That Fits the Evidence
Architecture advice should end in an operable change, not a diagram. An assessment should map critical journeys, domain and data ownership, team topology, deployment coupling, service objectives, incidents, capacity, security boundaries, cloud cost, and the changes that currently wait on coordination. It should distinguish a code-structure problem from a deployment, database, platform, or organization problem.
GARNO.TECH helps teams design new systems, modularize existing applications, and extract services when evidence supports the move. The work can include domain mapping, architecture decisions, dependency analysis, API and event contracts, data separation, infrastructure and CI/CD, observability, resilience, migration sequencing, acceptance measures, and transfer to internal owners.
A useful assessment produces a decision record and a sequence, not a wholesale rewrite estimate. It identifies the first boundary or internal improvement, measurable acceptance, dependencies, operational owner, rollback or coexistence plan, and the baseline against which benefit will be judged. It also exposes work that architecture alone cannot solve: unclear product ownership, overloaded teams, missing quality practices, unreliable data, or incentives that reward starting rather than finishing.
The recommended outcome may be a stronger modular monolith, a hybrid system, or a service architecture. The smallest responsible option is the one that addresses today’s limiting constraint, keeps the next change safe, and has people prepared to operate it. Revisit the decision when domain boundaries, team structure, workload evidence, or service objectives materially change.
Publications
Our research
Research and development of AI-powered solutions to optimize business workflows and enhance decision-making processes.
Analysis of machine learning models for predictive analytics in finance, e-commerce, and SaaS platforms.
Exploration of natural language processing and computer vision technologies to strengthen automation, personalization, and customer support.
The Future of AI in Enterprise Software: From Copilots to Governed Workflows
A practical guide to the next enterprise AI architecture: assistants, bounded agents, model portfolios, retrieval, evaluation, security, human authority, cost control and regulatory evidence.
10 min read
24 Jul 2026
Cybersecurity Trends: Turn Threat Signals into Business Decisions
A practical guide to the cybersecurity trends businesses should act on: AI-assisted social engineering, identity attacks, ransomware disruption, software supply-chain risk, cloud and API exposure, machine identities, Zero Trust and tested resilience.
9 min read
24 Jul 2026
The Business Impact of Custom Software: Value, Risk, and Ownership
A decision guide to custom software: identify the constraint, compare buy and build options, redesign operations, control data, improve customer journeys, model lifecycle ROI, and preserve long-term ownership.
9 min read
24 Jul 2026